Got a tip for us?

macOS

Because of the fraught nature of putting your devices or services on them directly in the path of the entire internet, it’s almost always the case that you can share files more easily, with more control, and more securely using a cloud-based sharing service, with a lot of provisos that I describe along with each service.

Each of these services partitions access, so you know precisely what you are letting someone view or download, and whether they can modify, delete, or upload files. You can set a time limit that a link will work, and usually restrict whether something can be downloaded or just viewed online. You may also be able to tell when they access or view files and see exactly what changes they make, if they have permission to modify files.

All the major tech companies offer them, and you may already have free access to substantial storage, or already be paying for a subscription plan or higher level of storage for other purposes.

All these services encrypt data at rest and use encrypted transport (HTTPS, primarily) for uploads, downloads, and link creation. However, if someone can access your account, they can view, delete, modify, download, and add files without restriction.

If you want to share files in a truly secure, end-to-end manner, however, the gold standard is end-to-end encryption (often abbreviated E2EE). With E2EE, the ecosystem you use generates and retains keys only at endpoints, on devices under your control. (Sometimes you’re involved in generating them, but usually the key creation and management is silently handled by the software.)

iCloud.com was never protected by E2EE before December 2022; after that, it became optional for some services if you enabled Advanced Data Protection (ADP). With ADP, iCloud Drive and other items synced, shared, and available via iCloud.com are protected by E2EE for you and with people with whom you share—so long as they also have ADP enabled. See how to turn on Advanced Data Protection.

Layer your own encryption on top

If you or your shared partners don’t have ADP enabled or can’t turn it on, you can layer E2EE on top of standard secure cloud services, because data that’s encrypted before transfer and stored in these locations remains encrypted, and is only decrypted by endpoints that have the keys.

That is, if you have an encrypted disk image and upload it, that integral encryption isn’t stripped off. If someone downloads the disk image, they still have to break the encryption applied to that data to access what’s inside.

But you can be more sophisticated than a disk image. Software that handles its own encryption—say, the password-management app 1Password—can safely hold and sync its separately encrypted data on a sync service. Someone stealing your 1Password vault has stolen trash.

As of 1Password 8, the app works only with its own syncing system. It used to work with Dropbox and iCloud.

Beyond software that uses E2EE for its internal format are packages that allow generic file sync by effectively tunneling the end-to-end encryption across a sync service! From your perspective, the files are readily available; to everyone in between you and your devices, including the sync services, it’s just a bunch of garbage-looking data. This is a nifty workaround.

I can’t recommend a service, as I don’t use any, but there are two options you can test for this purpose that are Mac compatible:

  • Cryptomator is an open-source solution to create an encrypted package, called a vault. It’s free to use on Mac, Windows, and Linux. The Android and iPhone/iPad apps have a one-time €19.99 (about US$23) purchase price to cover development costs.
  • VeraCrypt is also free, open-source software for creating virtual encrypted disks or partitions. However, the project supports desktop operating systems only: Linux, macOS, and Windows.

Cloud sync services usually reduce data transfer required by syncing only changed portions of files. (Unix folks call it the diff after a command-line tool; delta encoding is a more exact technical term.)

With encrypted files you upload, large portions of the file or the entire file change whenever it’s modified, resulting in a lot of data synced. However, Apple’s bundle form of disk images and some third-party software breaks large files into smaller ones to solve this problem. Only those sub-portions are changed, resulting in less syncing.

Encrypted messaging with others

Apple enabled E2EE with Android users for messaging over RCS, an industry standard Google championed. However, be sure to check when you start messaging with someone using RCS that their Android device has RCS encryption enabled. You can see whether it’s enabled in Messages: an Encrypted label appears at the top of the conversation, or inline if the encryption method changes. (If you had an ongoing conversation with someone over RCS, upgraded your device, and they have encryption enabled, an inline message in the conversation would appear.)

If you want to use E2EE to exchange data with others, you can use options like GPG Suite ($23.90 per year, 30-day trial, Mac only), which manages public-key encryption data for you, and lets you exchange encrypted files via email with anyone else who uses PGP- or GPG-compatible software. (PGP is a decades-old implementation of public-key encryption; GPG is the GNU, free-software version.)

If you trust other parties to manage the process, you can use iMessage or Signal. In early 2021, Apple quietly overhauled iMessage’s innards to make it more robust, but still needs to publish its spec and allow outside auditing. The company quickly had to patch major exploits found in their update in September 2021, making an even better case for allowing more eyes on the problem.

In May 2025, people were baffled that they couldn’t type “Dave & Buster’s” and similar ampersand-containing names into Messages. Turns out, Messages transformed the ampersand into something that triggered the protection! Apple fixed it, but it showed it worked?

Despite Apple’s lack of full transparency, iMessage remains trustworthy. Signal is created by an organization devoted to privacy, and has proven itself a great way to avoid interception.

What if you’ve lost your Apple hardware and it’s in a place where it can’t reach a Wi-Fi network and either has no active cellular data plan or can’t reach a cellular base station? What if it’s stolen, and the thief has disabled network access through Control Center? What if you stuck an AirTag or other Find My item on your backpack and left it where you can’t remember—or it was taken from you at an unknown time?

Apple’s solution is anonymity-preserving crowdsourcing that relies on the billion active devices their customers use worldwide, running recent-enough versions of iOS, iPadOS, and macOS to participate. The system relies on devices that can’t connect with the internet or a paired device to begin transmitting an anonymized, encrypted Bluetooth network signal that other Apple hardware can pick up.

A user's iPhone 17 Pro shows a screen that reads

Find My crowdsourcing causes every supporting device or item to emit a Bluetooth beacon that incorporates an encrypted hardware identifier.

This ID changes at regular intervals to prevent the privacy or safety nightmare of a third party tracking you, your devices, or your items through a persistent ID. Even Apple doesn’t really know where your devices and items are when using crowdsourcing!

When a device or item sends this beacon varies between Apple devices and Find My items:

  • iPhone, iPad, Mac, or Apple Watch: Find My must be enabled on the device (including the Find My network option), and it must be unable to make a connection to the internet.
  • AirTags and other Find My items as well as Apple and Beats audio hardware: If the audio hardware is within Bluetooth range of its paired device, it acts like a device, relaying its location through it. When beyond that range, it broadcasts a Bluetooth beacon as if it were a Find My item.

While 2nd-generation AirTags have minimum operating system requirements to appear in Find My apps, there is no such issue for the Bluetooth signals they broadcast. Any device that can relay a 1st-generation AirTag’s location can relay that of a 2nd-generation AirTag. (See AirTag 2 vs AirTag.)

The original AirPods rely solely on Bluetooth-based location tracking. When within Bluetooth range, they appear in the Find My app under Devices. However, they don’t work with the crowdsourced network. You can’t mark those audio devices as lost, and you can find those devices only within range of their paired iPhone or iPad.

What Apple can and cannot see

This broadcast is recognized by anyone’s iPhone, iPad, or Mac running at least iOS 13/iPadOS 13 or macOS 10.15. If a device owned by another person has an internet connection, it encrypts a package containing the beacon’s name and location information obtained or inferred, and uploads it to Apple.

That information is stored in a very particular way:

  • Apple doesn’t track what IP address or device uploaded it.
  • Apple doesn’t know to which device or Find My item any Bluetooth ID is associated—only your hardware retains that.
  • Apple doesn’t have encryption keys to extract location information.

It’s a beautiful system, in that no one—not Apple, the other equipment’s owner, or anyone sniffing in the area near your device—can determine who the hardware belongs to.

In the right circumstances using an iPhone, iPad, or Mac native version of the Find My app (see Precision Finding), you trigger retrieval of this location and timestamped location:

  • The Find My app uploads a cryptographic secret that Apple can match against the encrypted bundles they have of Bluetooth ID and location.
  • Apple’s servers transmit matching entries to the requesting device.
  • Using a locally stored encryption key that only your devices possess, the bundles are unlocked to determine the last location found.

What you get back

Find My provides this information in two different ways depending on the hardware you’re using:

  • iPhone, iPad, Mac, or Apple Watch plus audio hardware: The current location appears as expected in the Devices view of a native Find My app. If the device has an internet connection (direct or via a paired device for audio hardware), its location is a directly provided one; if it’s not connected to the internet, the Find My location appears when you use a Find My app.
  • AirTags and other items: The current or last-tracked location of a Find My network item, whether from a paired device or anyone else’s Apple device, is always shown in the Items view of the Find My or Find Items app. If you mark these devices as lost, you have more options: see what someone sees when they find your lost device.

In contrast to the Find My Device service, the Find My network is almost entirely one-way: you can determine where something is, but an owner can’t send a signal to the device unless it’s within Bluetooth range of an owner’s device. It also can’t be locked or erased as with internet-based Find My actions; See how to play a sound on a lost device or AirTag.

There are two actions you can perform as the owner of a Find My item:

  • When marking an item as lost, you can provide a phone number that Apple also stores securely. Someone finding the item can retrieve that data from Apple.
  • When you are near enough to connect to an item from one of your devices via Bluetooth, you can play a sound on it. This is particularly useful for finding a lost item in a classroom, home, or car, or for being notified of one nearby.

If someone’s iPhone or iPad detects that a Find My item or a Google Find Hub item is moving along with them—determined by Bluetooth proximity and across time—they are offered the opportunity to play a sound. That signal is sent via Bluetooth. (The same is true for an Android device detecting an Apple Find My item.) See what an “AirTag Found Moving With You” alert means.

Apple Designed the Find My Network To Deter Stalking

You might conclude that the design of the AirTag and other Find My items is both great for finding your own lost or stolen stuff—and a way someone might deploy tracking against you.

Fortunately, Apple included design elements in their Find My network for AirTags and third-party gear to try to protect the privacy of those who might be under observation without their knowledge, or who wind up accidentally transporting them. I dig into this in depth in Understand Stalking via Tracking.

Industry-Wide Anti-Stalking Standard Launched

Apple developed their system independently, though it offers a license and access to third parties. Facing criticism from a range of politicians and groups about stalking by tracker, Apple and Google—joined by several smaller firms—released a plan for interoperable industry support for identifying trackers across networks that went into effect in operating system and item updates in 2024. For more, see Active Stalking and an Industry Alliance.

You can also enable separation alerts. This feature notices when any Find My device or item is no longer in proximity to your iPhone or iPad. This might happen if you leave an iPhone in a coffee shop or it slips out of your pocket in a movie theater or you forget you put your iPad in an airplane seat’s unhygienic publication pocket. I explain separation alert management in Notifications for Devices and Items.

Google’s Find Hub offers a competing, non-interoperating ecosystem. Apple and Google don’t share location data with each other’s networks. But Android phones, iPhones, and iPads detect unwanted trackers across both ecosystems. See how to check whether someone is tracking you.

Activation Lock is an Apple feature designed to deter theft by preventing erasing and re-using an iPhone, iPad, Mac, or Apple Watch that has Find My enabled. While someone can still erase a device with Find My turned on, they are unable to activate and use the iPhone or iPad without having the Apple Account password for the account with which the device was used. Thieves have some hardware tricks to bypass this, unfortunately, but they don’t always work.

A device with Activation Lock active can still be tracked via Find My even after it’s been erased! And Apple will display a screen to any potential buyer or other user that the device is locked, deterring thefts and duped buyers.

Activation Lock was first released in 2015, and works with the iPhone 5s and later and iPad Air and later. An Apple Watch needs to run watchOS 2 or later. Macs models that support Activation Lock must either have a T2 Security Chip (Intel) or use an Apple silicon processor; in either case, macOS 10.15 Catalina or later must also be installed.

Even AirTags have a sort of Activation Lock—the Find My Lock—which is covered in how to reset an AirTag.

To avoid this when selling an iPhone (or associated Apple Watch), iPad, or Mac, disable Find My before erasing, which requires entering the associated iCloud account’s password. (Apple prompts you to disable Find My before letting you erase your device.) You can also disable it via iCloud.com after a device is out of your hands. Once you disable Find My, tracking is off.

If you haven’t disabled Find My on a device and you lose access to your Apple Account, the device remains permanently locked as well.

When purchasing any used Apple hardware, ensure that Activation Lock was disabled before you pay!

Remove a device from your account

You might see devices in this list that you or your family member no longer possess or that no longer work. You can remove these items from your Apple Account in any of several places. This removal also disables Find My on the device if it’s connected to the internet or the next time it connects.

Starting with the version 27 releases, use your iPhone, iPad, or Mac if you want to remove a device. (Previously, Find My was the better place to start.) Go to System Setting/Settings > Account Name, then scroll to the bottom. You then tap or click Remove from Account. You’re prompted with an improved warning in the version 27 releases:

  • In any version 27 operating system, Apple asks “Still Have This Device?” and defaults to a big blue OK button. To further discourage you, the dialog explains you should go to the device and sign out directly. Otherwise, tap or click Start Removal.
  • In the version 26 releases and earlier, you’re given a briefing on what happens if you remove the device. Tap or click Remove to proceed.

Apple once warned you that “This Mac will reappear if it connects to the Internet and Find My is turned on.” That warning was clearly inadequate about the consequences!

Some devices may offer a removal button in the Find My app on an iPhone, iPad, or Mac. The Find My app appears to be the only way to remove your AirPods from an Apple Account. However, in both the version 26 and 27 releases, I found it inconsistent and confusing why I was sometimes given a Remove from Account or Remove button, and at other times it was dimmed or resulted in an error message.

For instance, I can’t remove my iPhone, even though I’m offered a button to do so. (This may be connected with Stolen Device Protection, but it’s not described that way.) The Find Devices web app on iCloud.com only shows Erase, not Remove, for all devices except my iPhone, and it produced the same error.

Nonetheless, if you’re in a Family Sharing group, you can remove people’s devices from their accounts via an iPhone, iPad, or Mac Find My app or Find Devices at iCloud.com. (Or remove your device from your account.) The Apple Account password for the device is required, and a second factor may also be requested.

The Apple Account website used to let you remove devices, but now it shows the same error in every case.

AppleCare+ needs Find My switched on first

Apple offers an extended warranty against loss and theft for iPhone, iPad, and Apple Watch owners in several countries: “AppleCare+ with Theft and Loss”; in some countries, it’s the only option for these devices. An iPhone plan is $9.99 per month. In the United States, you can also enroll multiple devices with AppleCare One, and any iPhone, iPad, or Apple Watch on that plan receives theft and loss coverage. These plans start at $19.99 per month for up to three devices with no yearly discount.

This theft and loss warranty covers hardware faults at no cost and breakage for a modest fee. In the United States, it’s $29 to fix an iPhone’s screen or back glass, and $99 for other damage.

For loss or theft of these covered models, you pay a bit more, like $149 for an iPhone or $129 for an iPad. They will even ship you a replacement phone if you’re outside your own country and in a covered country! (You can get replacements only twice in any 12-month period.)

However, there are two key requirements. First, Find My Device must be enabled before a loss or theft occurs. Second, your device must remain associated with your Apple Account until a customer service representative tells you to remove it.

When you call AppleCare customer service to report the loss or theft, a representative guides you through erasing your device via Find My (see how to erase a lost iPhone or Mac remotely), disabling it remotely (Apple doesn’t explain what this means), and then “transferring ownership” to ensure no one can reclaim a “lost” phone later. Read the fine print if you sign up for this warranty option.

For those at high risk of being directly and individually targeted by spyware—for example, if you’re a journalist, politician, human rights advocate, or political activist—Lockdown Mode should be on your radar.

Governments, criminals, and industrial espionage agents typically deploy spyware against uniquely identified, high-value targets. Spyware, which largely relies on zero-day exploits, can be deployed as easily as texting someone a message, even if the message is never read.

With spyware installed, a remote operator may be able to exfiltrate (remotely copy off your device) all your data, access your microphone or camera without tipping you off, intercept messages sent by secure apps directly on your device, prevent messages from being sent or reaching you, plant evidence, and much more.

Apple considers spyware a significant violation of personal privacy. While in some countries there are legal methods to deploy spyware, it’s often used in contravention of national laws within countries and for national-security purposes or to violate the human rights of citizens or residents. Often, spyware is used by one country against those living in another country, including travelers, emigres, exiles, or refugees from the first country. China is notorious for pursuing current and former Chinese citizens living abroad. Apple funds researchers who try to uncover the use of this kind of software and protect against it, as part of their internal security work.

As a further effort to block intrusion, Apple added Lockdown Mode, a sort of super-firewall to resist known pathways for exploits by those who find themselves targets. Lockdown Mode works on an iPhone, iPad, Mac, or Apple Watch.

With Lockdown Mode engaged, your device will filter rich incoming media, block metadata, and prevent you from receiving invitations to any of Apple’s services. Messages blocks attachments and will receive and display only text and images, while disabling links and link previews. In Safari, Apple disables certain browser-based features that allow sophisticated code to run in web apps. (You can add exceptions and manage them, too.)

Starting with Apple’s version 26 operating systems, Messages always automatically disables links to URLs and phone numbers in messages the app identifies as spam.

Lockdown Mode also blocks incoming communications and invitations from people with whom you haven’t previously initiated contact. That is, if someone called you via FaceTime and you spoke with them, they will be unable to call you with Lockdown Mode on. If you called them in the past, however, they’ll be able to. SharePlay and Live Photos are also disabled.

Apple also blocks the installation of configuration profiles, often used to shunt network traffic for interception and to bypass security rules, and a device can’t be enrolled in mobile device management (MDM), commonly used in organizations to manage devices; MDM allows remote configuration and the overriding of user settings.

You can’t join a Wi-Fi network when Lockdown Mode is enabled unless the network has a password set. Also, the location is removed by default from images or videos shared in Photos, and Shared Albums aren’t available.

On the hardware side, you have to unlock your device before attaching to a computer or any accessory via the USB or Thunderbolt port. On a Mac, all accessories must be approved, independent of your option for accessory attachment described in the Mac settings worth changing.

How to turn it on

If you are one of those targets or just want to try out this technology, it’s simple to use. Here’s how to turn it on:

  1. Go to System Settings > Privacy & Security > Lockdown Mode and click Turn On next to the Lockdown Mode label, or go to Settings > Privacy & Security and tap Turn On Lockdown Mode.
  2. At the warning screen, read through the extensive list of limitations, and then click or tap Turn On Lockdown Mode. (Click Cancel to exit, or tap the close button.).
  3. Apple provides one additional warning that Lockdown Mode should be enabled on all your devices, and prompts you to click Turn On & Restart—or click Cancel to exit.
  4. Enter your administrator password and click OK. (You may be prompted earlier in the process for this password.)
  5. Your device restarts. On all other devices linked to the same iCloud account you receive a notification or popup dialog that prompts you to restart with Lockdown Mode. You can exit the dialog or click Later. You may receive this warning multiple times at intervals.

Living with Lockdown Mode

After your device restarts and you log in or enter the passcode, you will likely notice few differences.

When you’re browsing in Safari, a Lockdown Enabled banner appears at the top of every page: on the toolbar for a Mac and below the Location bar on iPhone/iPad. If you want to add a given site to the list of ones excluded from Lockdown strictures, Control-click/right-click in the address bar on a Mac and choose Settings for site name. Uncheck Enable Lockdown Mode. On iPhone/iPad, tap the Page Menu button in the address bar and tap the More button, then disable Lockdown Mode. You’re prompted to confirm your choice with an explanation of what that means. The banner on that page now reads Lockdown Off in red type.

You can change which websites are excluded from Lockdown Mode in Safari > Settings > Websites > Lockdown Mode on a Mac. This view shows both open websites and those you made a choice about. In this context, On means that the site has Lockdown Mode protections enabled, while Off means you have disabled any such protections for that site.

On an iPhone or iPad, go to Settings > Apps > Safari > Lockdown Mode, where you only see websites listed that you specifically disabled Lockdown Mode protections. Website exclusions don’t sync across platforms, either.

Outside of Safari, you’ll notice the difference when you attempt to perform an action that’s not permitted in Lockdown Mode. For instance, try to install a profile or view a file attachment in Messages, and you see descriptive error messages.

After you restart with Lockdown Mode disabled, you still won’t be able to open anything blocked in Messages on that device. Double-click a file and you see the same error.

To disable Lockdown Mode, follow the steps above and click Turn Off or tap Turn Off Lockdown Mode and then confirm by clicking or tapping Turn Off & Restart. You should be asked to authenticate via Touch ID or using a password. Your Mac restarts as normal and has full functionality re-enabled.

Apple’s withdrawn lawsuit

Apple sued an Israeli company offering spyware software to governments, but abruptly withdrew the suit in September 2024. They said in their filing, “Any disclosure, even under the most stringent controls, puts this information at risk. Due to the developments since this suit was filed, proceeding forward at this time would now present too significant a risk to Apple’s threat-intelligence program.”

You can track down your AirPods, AirPods Pro, AirPods Max, and Beats audio devices nearly as easily as other hardware. Here’s a rundown on what makes audio devices different than an iPhone, iPad, Mac, or Apple Watch.

Each earbud is tracked separately

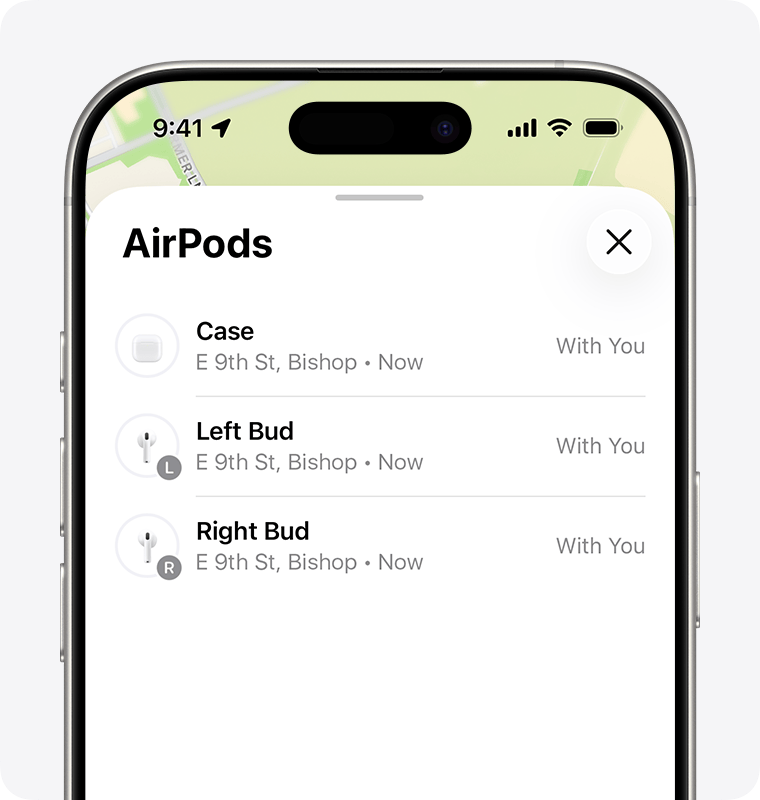
AirPods (3rd generation), AirPods 4 with Active Noise Cancellation, and AirPods Pro (any generation) can be tracked by their left and right earbud. If your earbuds are separated, after a short while, they appear as Left and Right entries in Find My. While you can use Find My on any device to search for them, I found the Mac’s display almost useless; use an iPhone if you can. After selecting the case or left or right earbud, tap Find.

Apple doesn’t provide Precision Finding, but uses relative signal strength to help you get close. You can play a sound on each individually, too, which lets you act like a bat and try to echolocate while using the proximity finder.

Which AirPods can be found how

Audio hardware is all located in the Devices tab or in a Find Devices app. Here’s what and when you’ll view and be able to select:

  • AirPods (1st and 2nd generation) offer only in-range Bluetooth tracking with a paired device.
  • AirPods (3rd generation), AirPods 4 with Active Noise Cancellation, AirPods Pro (all generations), and AirPods Max offer Bluetooth tracking.
  • Several Beats models track via Bluetooth and the Find My network.

Which Beats devices support Find My network? Beats Studio Buds, Beats Flex, Powerbeats, Powerbeats Pro, and Solo Pro.

You can carry out just two actions for all audio devices:

AirPods (3rd generation), AirPods 4 with Active Noise Cancellation, AirPods Pro, and AirPods Max also offer:

Audio devices that can’t be found except within Bluetooth range show just Play Sound and Directions.

Find your lost AirPods with Find My

  1. Open the Find My app on your iPhone.
  2. Tap Devices, then choose your AirPods. If your AirPods are out of the case, you might have to pick the left bud or right bud. With AirPods 4 (ANC) or AirPods Pro 2 and later, you can also separately mark each of your AirPods and the case as lost, in the event that you lose just one or your AirPods are separated from the case.

If your AirPods are separated, choose which bud that you want to find.
3. Find your AirPods on the map.

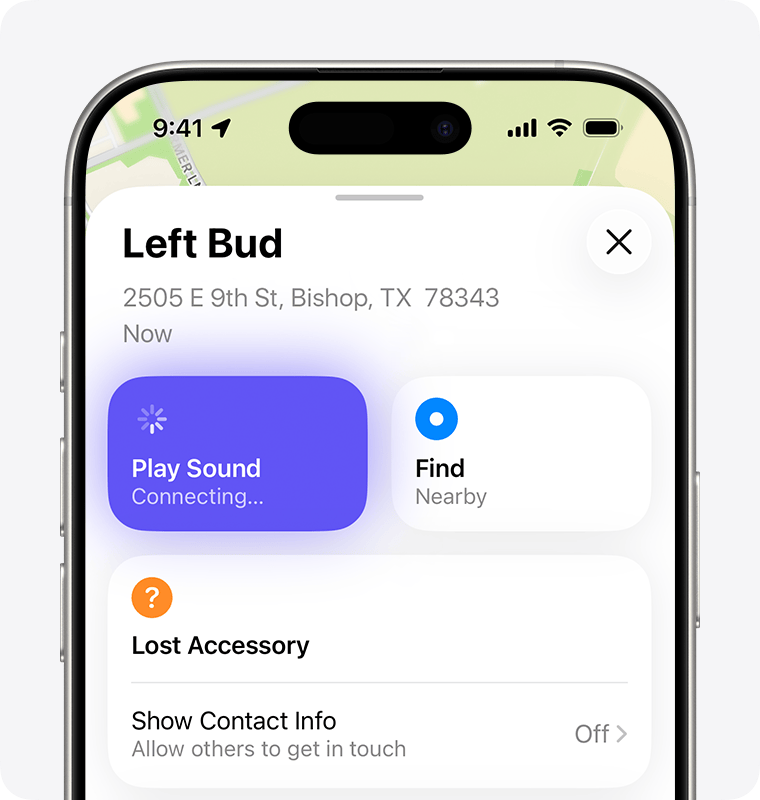
When your AirPods are nearby, tap Play Sound and listen for the series of beeps.

  • If they aren’t near you, tap Get Directions to open their location in Maps.
  • If you’re nearby, tap Play Sound and listen for the series of beeps.
  • Depending on your AirPods or iPhone model, you might also see an option to Find Nearby. Tap it, wait for your AirPods to connect to your iPhone, then follow the prompts to find your AirPods.

If you don’t have an iPhone or other Apple device to use Find My, you can also find your AirPods at iCloud.com/find — but the experience might be different and some functionality might not be available.

If your AirPods are “Offline” or show “No location found”

  • If your AirPods are out of range or need to charge, you might see their last known location. You might also see “Offline” or “No location found.”
  • You might be able to get directions to their last known location — but you won’t be able to play a sound or use Find Nearby.
  • If they come back online, you get a notification on your iPhone (or other Apple device that you use them with).

If you can’t find your AirPods

  1. Launch the Find My app, then choose your AirPods and swipe up.
  2. Under Lost [device], tap Lost Mode or Show Contact Info.
  3. Follow the onscreen steps to display your contact information. This allows someone to contact you if they find your AirPods.

Be ready next time with the Find My network and Notify When Left Behind

Want to help make sure that you find your AirPods next time?

  • The Find My network is an encrypted, anonymous network of hundreds of millions of Apple devices that can help you find your AirPods, even if they’re offline. Nearby devices securely send the location of your missing AirPods to iCloud, so that you can find where they are. It’s all anonymous and encrypted to protect everyone’s privacy. To make sure it’s turned on: On iPhone, open the Settings app, then tap Bluetooth. Tap the More Info buttonNo alt supplied for Imagenext to your AirPods, then scroll down to Find My network and make sure that it’s turned on.
  • With Notify When Left Behind, your iPhone or Apple Watch can alert you when you leave your supported AirPods at an unknown location.

Turn on Notify When Left Behind to get notifications if you leave your AirPods behind

If you still can’t find your AirPods, you can buy a replacement.

The Find My network might be unavailable in some countries and regions due to local laws.

It’s easy to see how Find My could be abused by someone trying to track a person surreptitiously. Someone with access or given too much trust can track a person or, via Family Sharing, track their devices. With Find My items, it can be even more insidious, although Apple built anti-tracking features into that network that they continue to evolve, including in cooperation with other tech companies.

There are three scenarios: tracking a person, tracking their devices, and tracking through a Find My item.

Someone following your location

Apple tries to balance safeguards against unwanted tracking with the utility that ostensibly most people use a feature for. When tracking people with Find My, Apple requires a transparent, consent-driven process when a person shares their location on an ongoing basis with someone else. (See how to get Find My alerts when someone arrives or leaves.) But even after someone has granted permission to be digitally followed, Apple requires more consent if their Find My follower wants to receive location-based notifications about when they arrive at, leave, or aren’t at a location.

Find My uses the People view to list all the people you follow or who are following you. While that seems like great disclosure and an easy way to control location tracking, it doesn’t address a few situations:

  • A non-savvy iPhone or other Apple device user could have people added to Find My without realizing it. This might be a stalker who somehow gains brief access to equipment or an untrustworthy partner. They might create a pseudonymous account that takes the name of someone you trust. Once set up, Find My doesn’t provide additional, ongoing information about person-based tracking. This contrasts with on-device location tracking on an iPhone or iPad, where you’re regularly asked whether you want to continue sharing your location with an app.
  • A domestic abuser, problematic ex-partner, or abusive parent who demands access to personal devices could add themselves to Find My tracking and require—under threat of violence—that you keep it in place. The new Hide Location option in Find My in the version 27 operating system releases offers what might be a safer alternative: you can pause tracking and resume it at will or early the next day. The other person sees only “No location found,” while you’ve paused sending your location. They’re not informed when you pause or resume. Of course, a truly dominating person may be constantly checking, and be provoked if your location disappears, too. (See how to stop or pause sharing your location.)

There is, of course, a completely valid case for parents wanting to track their children at any age while they are minors and living under their strictures, however lax or tight—but that’s a separate matter from a parent or guardian who uses that information not for safety or conforming to promises or rules, but instead as an excuse for abuse and control of the child.

If you’re in the first group or know someone who is, ensure you or they have strong device protection and potentially check Find My from time to time to make sure only names appear they know about.

See how to stop or pause sharing your location for how to stop sharing with people you don’t want to.

When a person who follows you sets up a notification to alert them about your movements, they first have to pass through a dialog that explains you will be informed of this attempt. This is partly a deterrent. Someone who sees it and does not want you to know should think twice.

If you’re the subject of such a notification, like someone setting up an alert when you leave your place of work, you see an alert on your iPhone. A similar notification appears if you have the Find My app open.

Pay attention to these notifications, as they’re the primary way you’re informed.

Someone following your devices

It’s harder to track people via Find My Device than either through their presence in People or an item as noted next. That’s because devices only appear in Find My in stricter circumstances and have more constraints:

  • Only an iPhone, iPad, iPod touch, Mac, or Apple Watch can be tracked as a device: While I’ve read about people setting up an iPhone and attaching it to a car, keeping it charged over time would be a poser, though I guess they could plug it into a charging port or tap into a port within the car body. There are much less expensive GPS trackers that last far longer, and Find My network items like AirTags that have extremely long tracking lives.

Someone could track Apple and Beats audio hardware that shows their location via a paired device or the Find My network, but this category of hardware has short battery life and short range compared to GPS-based trackers with Apple devices for relaying at short ranges.

  • You must be signed in on a device or iCloud.com with an Apple Account: With the additional validation step of two-factor authentication enabled on nearly all Apple Accounts, it’s far more difficult to manage to sign in to someone else’s account.
  • Only your own and Family Sharing devices appear: You can’t add arbitrary devices, as they have to be registered to your Apple Account or, with a Family Sharing group, someone else in that group. While Find My trackers are similarly locked, they have the advantage of battery life and size.

The only warning here? Check to make sure that no odd devices appear in your list of devices, and heed any warnings about devices being added to your account.

Unwanted tracking by a hidden AirTag

Find My items use little power, don’t require a clear path to a satellite navigation network or cellular network, and are tiny. They can easily be hidden, and could track someone across a long period. (Apple applies the same rules to third-party devices as their own.)

The same things that make it possible for someone to be alerted when they accidentally have something with an AirTag or other item in or attached to it—or they stole it!—also may help prevent people from being tracked by stalkers, domestic partners, private detectives, and celebrity hunters, among other categories.

Here’s how to extract information about unknown trackers:

  • Traveling with you: An item traveling with you results in an alert described in what an “AirTag Found Moving With You” alert means. You can then pause that device’s capability to track you or find the item and disable it. (See how to reset an AirTag.)
  • Identify Found Item feature: With an iPhone or iPad, you can use the Find My app’s Identify Found Item link in the Items view. See how to identify an AirTag you have found.
  • Interoperability: With an Android 6 or later device with an update from mid-2024 installed, the device’s owner will receive “moving with you” alerts from any Apple Find My network items; see how to identify an AirTag you have found. Likewise, an iPhone or iPad user with iOS 17.5/iPadOS 17.5 or later installed receives alerts about Google Find Hub network trackers moving with them. See how Apple and Google detect an unwanted AirTag.
  • No Apple hardware: If you don’t have an iPhone, iPad, or Mac with you (or there’s no active network), other devices you may be carrying won’t relay the item and enable tracking. Likewise, even though you can detect unwanted Google trackers, they aren’t relayed through your Apple devices. That sounds like a solution, but if you live in or travel through anywhere other people’s Apple hardware is close enough, those devices will upload tracking updates. That includes driving on a highway or riding public transportation.
  • Separated device alert: If the Find My item’s location is being relayed by other devices around you, however, it will make a sound in the right circumstances if it’s moved between 8 and 24 hours since it last checked in with its paired device to alert you to its presence. See what an “AirTag Found Moving With You” alert means.

Apple once promised an update that would alert you when a separated device is nearby on an iPhone or iPad, with an option to play the sound again or use Precision Finding. That apparently never rolled out.

Apple adding location sharing to Find My items might make it easier for someone to track you without alerts. Someone could place a Find My item in your stuff or a vehicle, then share the item with you and accept the invitation on any of your devices to which they had access when unlocked or if they knew how to unlock it; or they could share one of your items with themselves without you knowing.

However, this is a two-way street: all shared devices appear in your Items tab. If you suspect a shared item, check the Items tab for ones you’ve shared or shared with you that you don’t recognize.

Where to get help

There are many organizations beyond law enforcement eager to help people trapped in situations of domestic abuse or child subject to violence and an unsafe environment. For adults in the United States, that includes the National Domestic Violence Hotline; for children or those concerned about their welfare in the United States and Canada, the Childhelp National Child Abuse Hotline.

For those being stalked, one starting point is Safehope. It’s more likely you will need the help of police or federal authorities. Local police departments have their own paths to navigate, but for online or cyber stalking, it may be better to start with the FBI.

If the person you are worried about may be watching your device, use one they cannot see. Removing a tracker or turning off sharing can be noticed, and advocates warn that it can make a situation worse rather than better, so it is worth talking to someone before you act.

Most advice covers how you manage your own equipment. It’s incredibly useful to know how other people interact with your stuff when it’s lost or stolen and they find it. This lets you understand how someone might reply to you—by calling, emailing, or posting a note in a neighborhood forum—and what they would see that led them to it.

What a finder sees on an iPhone or Mac

Once the action is sent to an iPhone, iPad, iPod touch, or Apple Watch:

  • If the device is connected to the internet and asleep, the next time it’s woken, a passcode must be entered to gain access.
  • If the device is online and in use, the operating system drops the user into the Lock screen where the passcode-entry dialog or keypad is shown along with any message or phone number that was entered when setting up Lost Mode.
  • If the device is offline, the next time it accesses any network with an internet connection, the passcode lock is put into place.

After a restart, or when the device is powered up after being shut down, your phone number or email address appears on the screen if you provided it, along with the preset message Apple showed during the lock process.

What a finder sees with an AirTag

Because Find My items lack screens, someone finding one that is not marked as lost can bring up certain information from it as described in how to identify an AirTag you have found. However, if you have marked your item lost, by enabling Share Contact Information, a person finding it can see the phone number or email address you entered when activating that mode.

If you find an item for which the owner hasn’t shared their contact information, or you can’t pull up a webpage associated with the device, you could post a description to find that person. Try any number of places: social networks, college forums, NextDoor, Bluesky, Craigslist, or a piece of paper posted around the neighborhood. Describe loosely where it was found and what it looks like.

Someone could confirm ownership of the found item by providing details only the owner might know, like what it was attached to, part of (like a bike), or found along with (like a handbag).

An owner can also provide good evidence of their identity by:

  • Serial number: An AirTag and some third-party devices have serial numbers inscribed in the battery compartment. An owner can pull up a serial number via a Find My app. (See how to identify an AirTag you have found.)
  • Phone number: If you can call someone, great, but if they respond via another method (perhaps their phone was stolen!), they can confirm either the last four digits of their number if the item isn’t marked as lost or their entire phone number if it is.
  • Play sound: If you’re comfortable meeting up with a potential owner who hasn’t fully convinced you, if you’re within Bluetooth range they can trigger the item to play a sound from any Find My app they possess.

Apple has extra cues for someone near any Find My item (or Google Find Hub tracker) separated from its owner to aid that person in realizing there’s a tracker near them, see what an “AirTag Found Moving With You” alert means.

What a finder sees with AirPods

While marking audio hardware as lost follows the same steps as marking an item lost—providing contact information—someone finding your AirPods (3rd generation), AirPods 4 with Active Noise Cancellation, AirPods Pro (all generations), and AirPods Max can obtain information a little more easily.

With any AirPods earbuds, someone can open the case near an unlocked iPhone or iPad. This displays the message that the earbuds are lost, including contact information. With AirPods Max, someone would have to try to pair the headphones with an iPhone or iPad.

Turn on contact info for an item

Under Lost AirTag for Apple AirTags or Lost Item for third-party Find My network accessories, you see Show Contact Info and Share Item Information starting in iOS 18.2/iPadOS 18.2 and 15.2 Sequoia. This also appears for some Apple audio hardware: AirPods (3rd generation), AirPods 4 with Active Noise Cancellation, AirPods Pro (all generations), and AirPods Max.

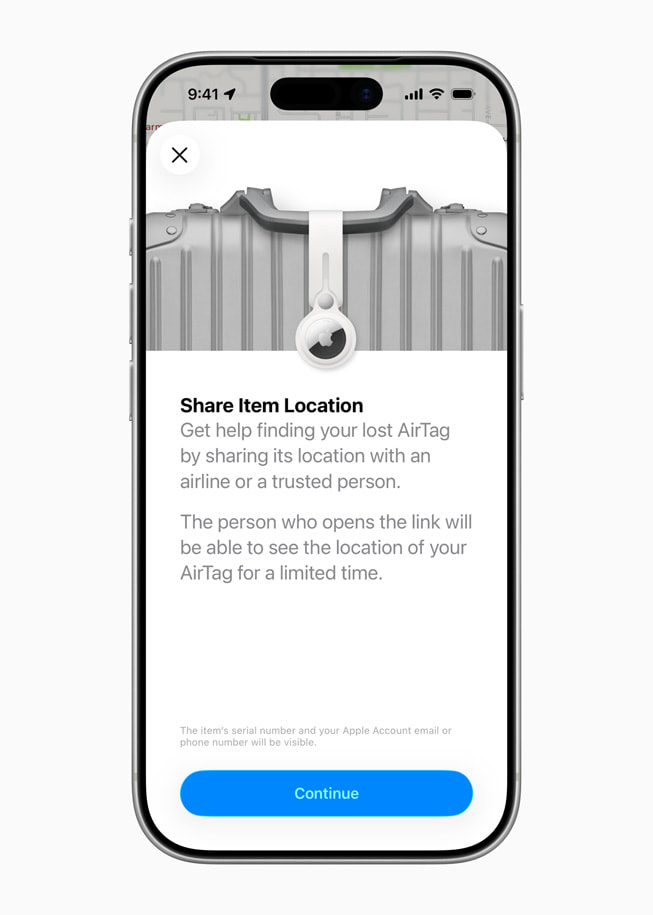
Show Contact Info is the item equivalent of marking a device as lost. For more on Share Item Information, see how to track lost luggage with an AirTag.

Using Show Contact Info effectively marks the item as lost, but because it lacks features available for hardware with a screen, I can see why Apple chose to relabel it.

Here’s how to mark an item or audio hardware as lost on an iPhone, iPad, or Mac:

  1. Beneath Lost AirTag, Lost Item, or Lost Accessory, tap or click Show Contact Info. (In macOS 26 and earlier with audio hardware, you can also Control-click/right-click and choose Mark as Lost.)
  2. After reading the details about what will happen when you turn on contact info, tap Continue.
  3. Audio hardware shows a more lengthy set of info. Tap or click the Close button to back out.

If the item is in Bluetooth range of any of your devices, you receive an error: “Item Is With You” that reads “This feature is only available for items that are lost and not located in close proximity to you.” You cannot proceed and can only tap or click OK.

On an Apple Watch, select your item or supported audio device, tap Lost Mode, and then tap the switch to enable it. You’re then prompted to enter a phone number or email address. (With watchOS 26 or earlier, use the Find Items app for items, and the Find Devices app for audio hardware.)

When an item’s or accessory’s status is updated, you should receive a notification.

When the device comes into proximity with you again—within Bluetooth range of one of your devices—sharing contact information is disabled. If you shared a temporary link, that link becomes inactive at the same time.

The Find My app’s Devices view and the Find Devices web app initially show a zoomed-out map plotting all your devices that are close to you and within reasonable proximity, as with people. If you’re in a Family Sharing group, you can see all devices of members in your group sharing their location with you. That can be quite a few devices. On an Apple Watch, you can only view a list and tap to see a map.

Any iPhone, iPad, Mac, or Apple Watch you own will appear as a device, along with all Apple and Beats audio devices. Because audio-device tracking has become more useful and differentiated over time, AirPods are covered separately.

The list is organized by person for Family Sharing with you at the top. As with People, each device shows the name assigned to it, a rough location, the last update, and its approximate distance from your location.

Your location is also plotted on the map as a blue dot if you’re near or between any of your devices, as is likely.

Find My doesn’t differentiate devices based on whether they’re located via an internet connection, proximity to your equipment, or the Find My network.

Select a device in the list or on the map, and Find My zooms in to center it in the map, typically showing it within a rectangle shaped by a radius of about 1/4 to 1/2 mile (400 m to 800 m). In the version 27 releases, select the device again to have the map zoom out.

You can take action on the device like this:

  • On an iPhone or iPad or macOS 27: Select a device and view the actions available in its sheet. Tap or click the close button in the upper-right corner to return to the full list.
  • On macOS 26 or earlier: After selecting a device, click the Info button to the right of the device name in macOS. Click anywhere but in the actions sheet in macOS to dismiss it.
  • On an Apple Watch: Tap the device and scroll down for actions. Tap the back arrow button to return to the main view.
  • On iCloud.com: A sheet appears in the upper-left corner of the webpage when you select a device.

Only the Directions options and the Notifications label (with different options) also appear in the People View.

Here’s what you can view or select from in Devices:

The top of the Find My sheet of actions shows a graphical depiction of the battery level for an iPhone, iPad, Apple Watch, or Mac laptop. Audio devices’ battery levels are not displayed.

Find My shows the device’s location on the map as a dot with its model icon above it. The dot is the center of a blue-shaded area if a device can be pinpointed; otherwise, the shaded area is larger and green. The shading radius indicates the level of confidence in the location.

Devices are listed even if they haven’t connected for months—or years! If it’s been longer than 24 hours, they appear as “No location found.” (For the full status rundown, see how to read the Find My app’s status labels.)

To remove old devices, see how Activation Lock protects a lost or stolen device.

Find a device you cannot reach

Here’s how to help someone else find their lost device—or find your own when you don’t have one of your devices at hand:

  • Family Sharing: Use the Find My app on a device or the Find Devices web app at iCloud.com from a group account with which the missing device’s owner has enabled sharing.
  • iCloud.com: For all other uses, turn to the Find Devices web app at https://www.icloud.com/find.

Some actions are limited: on the sheet for a device, you can play a sound, mark as lost, or enable notifications when found for your or anyone’s device using the Find My app on any device in the Family Sharing group. To erase a device, Find My prompts for the Apple Account password of the associated account.

If you cannot pass two-factor authentication

Apple requires two-factor authentication (2FA) for nearly all Apple Accounts—it’s useful in resisting account hijacking. However, it complicates using Find My if you (or someone you’re helping) don’t have access to any trusted, or Apple Account-linked, devices or phone numbers. Here are three approaches to set up in advance:

  • Add a trusted phone number for people you trust: You can add a phone number for a partner, family member, close friend, or even an attorney or other professional you could contact in an emergency. Then, as long as you remember your Apple Account password, you can select that other person’s phone number in the 2FA validation process and they can provide you the code.
  • Create a passkey for your Apple Account: Apple lets you bypass two-factor authentication if you enable a passkey. While a passkey is typically stored on your iCloud-synced devices, you can use some password managers to store one instead.
  • Use a hardware encryption key: Apple lets you rely on hardware encryption keys for Apple Account access. As long as you still have one of the keys you set, you’re not locked out of iCloud.

Malware describes a broad category of unwanted software that is installed without your explicit knowledge, and which carries out tasks beneficial to the operator and creator of the malware, and detrimental to you, your local network, your friends, family, and colleagues, and potentially strangers and even the whole of the internet.

Malicious software can be as “benign” as adware, which is bundled with software you intended to install, and which redirects your browser to a portal through which the adware’s creator earns commissions when you search or make purchases; or which overlays or replaces ads on pages you view to earn income on your stolen time (also effectively stolen from the sites you visit).

But it can also be quite hostile: it might encrypt all your files and demand a ransom (more on that below), delete your files, or use your computer to launch attacks. Malware often tries to find other devices reachable on the same network—often which are more susceptible to network infiltration than from attacks launched over the internet—to infect them with the same software.

The main point is that you don’t want any software to run on your Mac that you aren’t aware of and haven’t given approval to run. What follows is the kinds of threat a Mac user faces; what Apple does about them and what you can do is separate, as is whether to install anti-malware software at all.

Why Apple avoids the worst of it

While the first widespread malware appeared on Macintoshes many, many years ago, Apple’s choices over the last 25 years have meant that Macs have been generally resistant to the most common vectors of attack that afflicted and still plague Android and Windows users, as well as people running servers of all types.

There are a lot of reasons for this, some of it due to system choices and some due to obscurity—the number of devices running each operating system.

Windows wasn’t designed with the internet in mind, nor the receipt of arbitrary emails from people outside an organization. For too many years, a successful exploit could hijack a machine by someone merely receiving (not even viewing) an email message or passively viewing a webpage. Microsoft has improved its security dramatically in Windows 10, the first release of which was 2015, but older versions—still in use on hundreds of millions of devices—still suffer from many attacks.

While Google built Android as a modern, Unix-based, internet-connected operating system, they made multiple interconnected errors that led to Android being highly insecure. Among other issues, they handed control to handset makers and carrier networks, making it difficult to push out security updates directly. They also rapidly revised and abandoned older versions, no longer releasing security updates, even while handsets were still being sold as new in the box that ran those versions. And despite the dangerous world into which Android was first launched in 2009, the OS seemed full of easily exploitable flaws that took years to move past. As with Windows, even if newer versions of Android are fairly secure (in relative terms), a billion older Android devices still remain on the market.

It’s in this space that Apple finds itself, with both iOS/iPadOS and macOS. Frankly, there are billions of better targets than any of those Apple operating systems. Apple didn’t have to engineer a system that was 10 times better than Windows, but just enough—better coupled with the substantially fewer numbers of Macs in use in the world—that malware creators targeted the low-hanging fruit instead.

While Apple has sold a lot of iPhones and iPads (and some iPod touches), the user base for Android and forked-Android phones and tablets (forked ones use open-source-derived variants) outweighs iOS and iPadOS copies by a bit under three to one—and Apple patches security flaws quickly. (Apple has closed that gap in recent years, but it’s the mass of older devices that remains the concern.)

Remember the old joke about a bear rushing toward two campers woken from slumber: one stops to put on his shoes. The other says, “You can’t outrun the bear!” The first replies, “I only have to outrun you.” Apple always ties their shoes.

The kinds of malware

Malware and its enablers come in a lot of varieties, and it’s worth knowing the terminology. Here’s a primer:

  • Virus: Malware that injects itself inside existing software, and executes whenever that software runs. It can spread by software being copied, such as an app being corrupted by a virus on a download site, so everyone who downloads it receives and runs an infected version. A virus can be a payload of a worm or Trojan horse, which install the virus.
  • Worm: Worms are free-standing malware that can spread themselves across a network, and may install other malware, such as viruses. The world’s first widespread malware was a worm.
  • Trojan horse: Malware masquerading as legitimate or desirable software that a user installs. It may result in freestanding malignant software or a virus inserted into otherwise valid software.
  • Phishing: A technique of convincing someone, typically via email, to hand over personal details, particularly payment information, by sending them to a malicious webpage that’s a close copy of a credible site.
  • Ransomware: Malware that targets user document files and encrypts them with a key that is discarded and only the attacker has access to. The attacker demands money to provide the key.
  • Bots: A bot is not a “robot,” but automated software that performs automated activity on behalf of its owner, which can include coordinated attacks against websites or servers, illegitimately clicking ads, sending spam email.

The most likely scenario for a Mac user to be infected by malware is through a series of seemingly innocent, chained actions: phishing, Trojan horse, virus, and ransomware. Often this has to be coupled with a form of understandable naïveté: bypassing Apple’s warnings and installing seemingly unknown software.

How an infection actually happens

Because I don’t want you to feel targeted in this story, let’s call the victim Bob. Bob is checking his email in Apple Mail or a third-party email app. Because Apple Mail has always been quite resistant to in-mailer attacks and most other mail clients are the same, Bob’s not at risk by reading messages.

But Bob sees a message about a piece of software he uses regularly. “Get a free 90-day trial of the new version of AliceDrawPlus! Click this link, and download and install. Because this is a special trial version, right-click the installer and click Open to make sure it runs!” (Real phishing email is often not that grammatically correct or well targeted, but some is.)

Bob isn’t thinking about unsigned software. Instead, he looks carefully at the email, which absolutely looks like other messages he’s received from Alice Corp. He downloads the file, bypasses Gatekeeper protections, and the Trojan horse he was phished to download runs and installs a virus.

Lest you think this is a problem I know about only secondhand, several years ago, one of my kids was having problems with their computer. I checked, and they had been fooled into installing an Adobe Flash “updater.” I had accidentally enabled administrator privileges on their account, and I had apparently never had the malware talk with them. We installed some anti-malware software, and fortunately the thing they’d installed was fairly benign.

But because the installer is running in Bob’s home folder, and not accessing or trying to install in a privileged location or make similar changes, it doesn’t trigger a request for an administrator password—although Bob might have entered that without worrying, too.

The software appears to install, but instead of launching, it claims there was a license problem, and the file was corrupted. “Check back in four weeks for another update!”

Meanwhile, as Bob continues to work, every file in his home folder, starting with Documents, is being encrypted and copied to a new file and then the original deleted. He may have no notion it’s happening, particularly if he has an SSD and can’t hear a hard drive working away like mad, though his fan might spin up unexpectedly.

macOS requires users to agree to allow apps access to certain folder locations, but because we have been trained to click OK most of the time, it might not raise Bob’s hackles or most of ours. See how to control which apps use your Mac camera and files.

A few hours pass and Bob tries to open a file. It has a strange extension. It won’t open in the app that created it, but when he double-clicks the file, he gets a message that explains all his files are encrypted, he needs to pay up, or the decryption key will be thrown away and his files lost forever.

Bob’s been attacked by ransomware, and his only way out may come if he has a backup history—or wants to pay the Bitcoin or other cryptocurrency the criminal demands.

If Bob were as credulous as depicted, he could just as easily have been phished, where he was presented with a website that absolutely looked like AliceCorp and told to enter his serial number and payment details for a huge discount. Phishing is a virus of the mind, and your Mac can’t help much against that.

ClickFix, the fake CAPTCHA

Bob is too clever to fall for the above, but he visits a website that flashes up a CAPTCHA, which is typically some text you are using your human eyeballs to perform OCR on or identify squares containing the same object (they are stealing our brain’s processing power here), or to solve a simple puzzle. Bob performs the sequence of actions he’s told to perform in the “CAPTCHA,” and he falls to phishing.

This technique, ClickFix, has been around since 2024, but apparently dramatically accelerated how often malware fighters detect it.

Why? Fiendishly simple. We’re so used to following the “orders” of a CAPTCHA, clicking images or solving puzzles, that this doesn’t seem that weird if we’re on autopilot.

However, it should go without saying—but I’ll say it—never paste anything into Terminal from a random source on the internet, whether it appears to have authority or not. I try to avoid it even here, because of the consequences of a Terminal-based command going wrong and taking a lot of your time to reverse.

Apple agrees, and rolled out an anti-paste warning in Terminal! Starting in Tahoe, if you have something on the clipboard that macOS deems could be harmful, you receive a warning that might cause you to think twice.

Apple can escalate further than a warning, blocking paste entirely if they’re sure there’s malware involved. Your Mac may also block a script from running for the same reason.

Ransomware is your biggest worry

While our theoretical friend Bob was fooled into installing malicious software and bypassing protections in the examples above, the risk to many people isn’t quite as straightforward as the above.

Before I dig in, I want to note that ransomware is your biggest worry, but ransomware remains nearly non-existent on Macs as Apple continues to crank up protections that make it increasingly unlikely to thrive—particularly while it’s easy to infect users of other platforms. Several of those are covered in how Gatekeeper decides which Mac apps can run and how macOS protects its own system files.

The reason I characterize it as the biggest worry is that it’s so blessedly simple to create and provides easy rewards for those who deploy it. Macs aren’t inherently resistant to it, but it feels as if they were. That luck could change with the right (“wrong,” really) exploit and timing.

You can see how with a phishing attempt like the above or email messages that tell someone a sequence of commands to perform, ransomware could be rolled out en masse to millions of people. Payments are quasi-anonymous to avoid easy tracking, and ransomware is effective against naïve and some more experienced users because it doesn’t seem like the way in which malware gets delivered and runs.

As noted above, when a ransomware app is launched, it encrypts all user files. The operation typically passes a file through an encryption algorithm, writes a new file with a new extension, and then deletes the source file.

Depending on the attack, you may get a message on screen when it’s done, explaining what happened. Some ransomware embeds the message into every file, so double-clicking provides the same text.

Send hundreds to thousands of dollars (or, as an organization, up to tens of millions of dollars) in Bitcoin to a specified address—kind of like a semi-anonymous post-office box—by the specified date and the hijacker will give you the key to decrypt it. Fail to comply, and they throw away the key.

Occasionally, white-hat hackers, who use their coding and online prowess for good, will crack open a ransomware scam and distribute passwords or a generic decrypting tool to victims!

Ransomware works on the portion of macOS (and any afflicted operating system) that contains user files and for which file and folder permissions more or less all belong to the logged-in user, as well as the partitioned-off part of memory that runs programs, called user space.

This is distinct from the system files and kernel space that contains all the components of macOS and in which the operating system itself runs. While crackers want to subvert system files and have software run with the highest permissions, that’s a hard lift—and why bother, when you can just use ransomware instead?

Here’s the other thing that should reduce your blood pressure if I just raised it: it’s also remarkably easy to mitigate the effects of ransomware (or any malware) with a little prep and ongoing work that’s not likely to exhaust your patience or wallet. The built-in measures come first, and then the question of third-party anti-malware software.
Find My lets you take a variety of remote actions on devices and short-range actions on items. Options vary in utility based on whether your device has fallen behind a couch cushion, or has been misplaced or stolen, and whether the device or item is directly reachable via a local network, the internet, or the Find My network. With devices, Apple follows up many actions with an email message sent to your Apple Account’s associated address.

You can set up notifications within Find My to provide a variety of information depending on the category:

  • People: You can opt to receive alerts when they arrive and leave locations you define, or send them alerts based on your location.
  • Devices and Items: You can be notified when a device is found if it’s marked as lost. You can also receive a prompt when you leave something behind.

People-based notifications let you track when someone (including you) arrives at or leaves a location. The alert can be set once or on a recurring basis. Here’s what to do:

  1. In a native Find My app on an iPhone, iPad, or Mac, bring up the sheet of actions for a person via the Person view.
  2. In the version 27 releases, beneath either Notify Me or Notify Person, tap or click Add Location Alert. In earlier releases, beneath Notifications, first tap or click Add, then select Notify Me or Notify Person.
  3. For Notify Me, you can select I Arrive or I Leave; for Notify Person, you can select Person Arrives, Person Leaves, or Person Is Not At.
  4. Pick a location. Some locations will be prefilled, such as you or another person’s current location.
    • You can also tap or click New Location, then drag on the map or enter a location.
    • Clicking or tapping in the search field brings up potential matches from the person’s contact card before you start typing.
  5. Optionally set a radius. Tap Small, Medium, or Large at the bottom of the map to switch among radii of 300, 800, and 1,250 feet (90 m, 240 m, and 380 m).
    • Or drag the blue dot at the right out to a preferred distance; a label indicates the radius as you drag.
    • The minimum is a 300-foot (90 m) radius. The maximum is 792,000 feet — 150 miles or 241 km.
    • A wider area prevents excessive notifications for departures, or gives earlier warning of an arrival.
  6. Your final option varies based on the Arrives/Leaves/Is Not At selection:
    • For yourself or someone else, Arrives/Leaves lets you pick Only Once or Every Time for notification frequency.
    • For another person with Person Is Not At chosen, you can set a range of time and days of the week.
  7. Click or tap Add to complete. If you set this up to track someone else, they now receive a notification that you’ve done so.

If you’ve asked your child to remain within a certain distance of home, or want to know when they’re returning so you can hide the liquor—er, clean up around you—then changing the radius is useful. However, an older child might employ a Cat in the Hat strategy towards a parent.

This map selection tool is also used with Notify When Left Behind, a way Apple helps you avoid accidentally losing stuff.

Is Not At could be useful with an employee or child to know when they’re not in a place you expect at certain times.

The other person is always told

When you let other people know what you’re up to with notifications, they receive an alert that tells them what they can expect to receive. This appears across your devices and is an anti-stalking measure; see how to check whether someone is tracking you.

Your Apple Watch lets you notify or be notified about people’s locations, but it’s limited to Notify Me/Notify Person with two options. You can notify someone when you leave your location or arrive at theirs, or when they leave their location or arrive at yours. You can’t select locations or set up other nuances below.

If you want to see notifications about someone else’s comings and goings, you’re told what they will be informed of and given a chance to cancel, and they receive a notification about what you’ll be updated about.

For recurring alerts set to Every Time, you’re told that someone has to approve the action. The notification is slightly different for Person Is Not At recurring alerts, specifying that the other person will be notified at the moment the schedule first goes into effect. So if you set the schedule to Wednesday at 9 a.m. and it’s Sunday night, the alert will say a request will be sent for approval at 9 a.m. Wednesday. (The time zone will be whatever time zone the location you set is in, not your or the other person’s current time zone.)

For notifications that require permission, you see a Pending Request label on that person’s sheet of actions.

It can be useful to pause notifications for a lot of reasons; tap or click Pause to pick a time to resume: either “Until the end of Today” or from a calendar.

You can freak someone out by creating a notification without alerting them first. When you use Find My to track someone’s arrival or departure, that person receives a notification that you’ve done so. This can happen in the most benign circumstances.

After my wife texted that she was coming home with oodles of groceries a couple of years ago, I created a notification to alert me when she got home so I’d break off what I was doing and go down a couple of flights of stairs to the street level to help her. She was surprised by the alert she had received. At that time, Apple had just changed their system to provide this disclosure to others.

That disclosure is quite useful, because tracking can be used in non-benign situations, too: see how to check whether someone is tracking you.