Got a tip for us?

If you open System Settings > General > Sharing, you’ll notice many resources your Mac can share with other devices on your local network—and, in some cases, beyond.

You can share your screen, files, printers, and internet connection, for example, and you can also enable various types of remote access to your Mac.

All these features can be handy, especially in that they enable multiple Macs in your home or office to talk to each other. You can copy a file from a Mac in the other room, or view what’s on the screen of the Mac upstairs when you’re downstairs.

However, Apple pairs easy local access with easy remote access: if your Mac is reachable from the internet, some services you share locally can be available remotely. Some may require a password, but that could be easily guessable if you haven’t been thinking about internet-based attacks. And just having certain services active, like Remote Login, could allow remote attacks if an exploit turned up in Apple’s system software, before such exploits were known and patched.

This isn’t speculative. Apple regularly patches exploits and bugs in low-level software, like sshd, the secure shell daemon, the system software that handles remote Terminal-style sessions if you have Remote Login enabled. Those flaws are usually fixed before anything terrible is unleashed in the wild, however.

How exposed you are comes first; which sharing services are safe to turn on follows from it.

What’s your risk of internet intrusion?

The most likely determinant of risk to attacks or intrusion via the internet is how directly reachable your Mac is. While the vast majority of routers have a public IP address, very few computers on local networks do. Almost always, your router receives traffic and then re-addresses it to your Mac.

A public IP address is by definition routable or reachable from the rest of the internet. The network of which it’s a part appears in routing tables traded among the devices that exchange data across this mighty global beast.

However, IP addresses can also be static or dynamic. A static address is assigned to a device and doesn’t change over time without typically manual involvement in changing settings. A dynamic address can change at will, and it’s automatic.

Private network addresses can be either static or dynamic; most of us have networks configured to assign the next available address when a computer, phone, or other device requests one. Some routers can be configured to assign static private addresses to specific devices.

If you’re not running a business network or paying extra, your broadband router typically has a dynamic public address. The ISP may rotate the address every once in a while, or if there’s a service outage or you restart the router, a new address is assigned.

The dynamic nature of these public addresses assigned to routers doesn’t aid in security in any fashion, because they’re still public. You might not be trackable by public IP, but your router is still reachable.

A public IP address is simply one that’s uniquely assigned across the internet, and can be reached from anywhere else on the internet. Your router almost certainly has a public IP address, because that’s how it interacts with the rest of the world on your behalf.

It’s a very low bar for any interested party to scan all the originally defined set of public addresses on the internet—yes, as many as hundreds of millions of them—to find open access for services that the scanner might know potential security exploits for, sometimes far out of date…but there are a lot of old, unpatched machines on the internet. Thus, with a public address, there’s no obscurity possible.

That “originally defined” part uses an addressing scheme called IPv4; a newer standard, IPv6, is more resistant to bulk scanning. See the IPv6 section below.

Most homes and businesses rely on private IP addresses for everything but their broadband connection’s router, however. These reserved ranges are only used on local networks, are managed by a router (using something called Network Address Translation or NAT), and typically assigned out automatically with DHCP (less well known as Dynamic Host Configuration Protocol).

Private addresses, which are usually in the form 10.0.1.x or 192.168.1.x, can be reached without any special effort by other devices on the same network of privately assigned addresses. However, when a device on your network makes a request outside its private network range, like viewing a webpage, the router rewrites the request to use the router’s public IP address, and sends it out; the router receives a reply and then forwards it to the locally connected device that requested it.

If you were to have a public IP address on your Mac—not just on your router—it would be like standing on a street corner instead of being inside a house with a locked door and a mail slot. Anyone can come up to and start talking to you or assault and rob you! (Unlike in the world of atoms, where violent crime is minimal and has drastically fallen in recent years, an internet mugger can attack targets wherever they are and a huge number simultaneously.)

The same effect happens if you configure your router to connect its public address with specific services on one or more devices on the local network. For instance, some people want to have a globally available web server or file server, and it’s not terribly hard to expose the correct connection. That makes that web server or file server just as exposed as if the Mac had a public IP address—but only those services, not everything else shared on the Mac.

NAT isn’t designed as a security measure: it’s just a spreadsheet the router maintains to wire requests and replies together. It’s incidentally a general security measure because it makes potentially exploitable open doors on your devices nearly impossible to reach without being specifically targeted, particularly with a router that can be subverted.

You may already be sure you don’t have a public IP address on your Mac: your ISP charges extra for public addresses you use beyond the one attached to your router, and you know you’re not paying for it; your ISP doesn’t offer public addresses; you specifically made sure you weren’t getting one from your ISP; or you’ve configured your router and you know exactly how you set things up.

If you’re not sure, walk through this list:

  • Check your Mac’s address: You can examine the IP address assigned for your active network interfaces. Go to System Settings > Network and select each of your active interfaces in the main pane:

— Ethernet and most interfaces show the address in the main pane under or next to “IP Address.”

— For a Wi-Fi interface, click Details to see the address next to IP Address.

  • Check your router: Connect using the administrative controls for your router, log in, and look at where your router shows its WAN (Wide Area Network), Modem, or Internet IP address, and how network addresses are handed out under DHCP, LAN (Local Area Network), or similar labels. The WAN side is almost always a public IP; the LAN/DHCP part almost always private.

If the IP address of your Mac or LAN/DHCP addresses on the router is in any of these ranges, it’s a private one, where x is any number from 0 to 255: 10.x.x.x, 172.16.x.x to 172.31.x.x, or 192.168.x.x. Otherwise, it’s almost assuredly public.

Type in “what’s my IP” at Google and it will tell you what it thinks your IP address is, and offer a list of sites that do the same (sometimes with more detail). However, if you’re in a DHCP/NAT scenario with private addresses, which is what nearly all home users and most business users are, the address shown on the website is the one associated with either your broadband modem or a further upstream router run by the ISP—not your Mac.

IPv6 adds a wrinkle

Technically, the IP address style x.y.z.a, like 192.168.0.1 or 36.44.0.6, is IPv4 (version four), which has been in use for decades. For nearly 30 years, internet mavens have been trying to migrate the networks that comprise the internet to IPv6, which has a lot of advantages. This includes more addresses that can be assigned, the so-called address space. Where IPv4 has billions of potentially usable addresses, IPv6 has hundreds of undecillions.

However, the trouble has been all the inertia of having billions of devices and hundreds of millions of routers and pieces of plumbing designed around IPv4. While the internet has largely retooled—after nearly 30 years—so that IPv6 works as well as IPv4, nobody wants to end the widespread use of IPv4 in residential networks and many company networks, because of private addressing. IPv6 was designed before NAT became broadly used and thought of as a quasi-security measure to prevent ingress to ISP and corporate networks.

For most of us, that means until private addressing can work in a similar way within IPv6, our ISPs have assigned our routers a public IPv4 address, and have chosen one of several paths with IPv6:

  • Ignored/disabled: Your ISP may simply not pass IPv6 traffic, and it’s not an issue for security.
  • Allow, but disabled by default: You can use IPv6, but you have to configure your router to allow it. My ISP requires a special router for its fiber-optic service, and has detailed instructions for enabling IPv6. Since I have no specific need of it, I’ve left it disabled to reduce my exposure on the public internet.
  • Turned on by default: You may have an ISP, like my editor Dave Johnson, who enables IPv6 by default through its system, and your router and devices all automatically get IPv6 addresses, just as they do IPv4 ones.

If you’re in that last situation, you may have publicly reachable IPv6 addresses—it can be hard to tell, because some ISPs use techniques that are similar to NAT. If the IPv6 addresses are truly publicly accessible, they expose the same general risk of remote attack as public IPv4 addresses and should follow the advice in the next section.

But some analysis suggests it’s not as bad as it might seem. The Internet Society has an interesting FAQ about IPv6 and security, and notes that attackers could find “infrastructure nodes” reasonably easily—the routers that form the backbone of the internet and connect ISPs, streaming services, data centers, and so forth all together.

But, the document explains, “It is generally unfeasible though to address scan a network for client devices, since their addresses are randomized over a very large address space.” Simplified, it means that it’s not a needle in a haystack, but 10,000 needles in a Nebraska-sized area of haystacks. (With IPv4, it’s a cubic foot of hay and you can see all the needles inside.)

If you’re truly concerned, you can disable IPv6, as it isn’t a mandatory or critical part of using the internet. Here are three possibilities, the first two of which will affect your entire network:

  • Disable IPv6 at the router: Find the manual for your router and follow instructions to disable IPv6. It may be as simple as selecting a radio button.
  • Ask your ISP to disable IPv6: Contact your ISP and ask them to disable IPv6 on your account or router if they control your router or have the ability to do this at a higher network level.
  • Disable IPv6 on your Mac: If you can’t or don’t want to disable IPv6 network-wide, disable IPv6 on your Mac. Go to System Settings > Network, select an interface, and click Details. Select TCP/IP and choose Link-Local Only from the Configure IPv6 pop-up menu. Click OK. This leaves other devices still reachable via IPv6, but at least locks down your Mac.

You can’t disable IPv6 on an iPhone or iPad.
If you lose your macbook you may want to locked it in find my to make sure no one would take it. When you find it, you may want to unlocked it. You can put in your passcode as normal and unlocked it. This may only allow you to use it as normal for a few minutes then it would suddenly go black and showed a lock. Whenen this happened, you won’t see any writing on the screen and entering your password won’t do anything. If you locked your macbook through find my and can’t unlock it now, here’s what you can do.

To unlock any Apple silicon Mac or an Intel Mac with a T2 Security Chip (models released starting in 2018), follow these steps:

You could be stuck if you’re using a Mac with multiple accounts that another account holder has Find My control over and that person locks it. You need them to perform the unlock in person or read you their passwords. This could be awkward.

  1. After marking the Mac as lost, it appears with a question mark overlaid in the Devices view.
  2. When the Mac restarts, it shows the macOS Recovery screen with Recovery Assistant appearing as the active app in the upper-left corner.
    • Apple claims the message you entered will appear at startup. It does not, in my testing.
  3. The account used to lock the Mac is the only one that appears. Click its icon and click Next. Only one account appears because only one account per Mac can be used for Find My.
  4. Enter the account’s password and click Continue. If you don’t remember your password or it doesn’t work, you can click the “Forgot all passwords?” link, which takes you to the FileVault Recovery process. Using that method, you can enter your Recovery Key, reset the password, then restart step 2.
  5. If you entered it correctly, “Authenticated succeeded” appears. Click Restart.
  6. The Mac restarts again into Recovery Assistant. This time the screen reads Activate Mac.
    • You reconnect with your Apple Account by entering its password.
    • You can select any macOS account that can log in to the Mac, provided you know the Apple Account shown next and its password.
    • Select the account, enter its macOS password, and click Next.
  7. You may be prompted to enter your full Apple Account email address; a Mac shows you a portion of it. Enter it and click Next.
    • Your Mac prompts you to enter the password associated with the partially displayed Apple Account address, or the one you just entered in full.
    • If you don’t have that password, click the link below the field, Use Device Password, and enter the last password used to unlock the Mac in a regular session before it was locked. In beta testing, I found I didn’t get a field to enter that password in, but this may have been fixed by the production release.
  8. On a successful entry, the Mac restarts yet again after a one-minute countdown. Enter your password when prompted to start up into a regular session. Apple Pay will have been disabled, and your iCloud sync is probably paused as well. When prompted, enter your Apple Account password (or passwords if you have multiple accounts linked to your macOS account).

The first time I tried this with macOS 27, I had to choose Apple menu > Restart after it wouldn’t proceed. Then I followed steps 5 and 6 above again, and it worked.

If your Apple Account gets locked

If you try this too often, as I did while testing, or for other security reasons only Apple knows, your Apple Account may be locked. At step 6, I was told I had to reset my Apple Account password from one of my other devices; all four of which are linked to the account were shown. I made that change. In one of the public beta versions, clicking Unlock Account did nothing before or after changing. I was able to click Cancel, complete step 6 again with the new Apple Account password, and proceed to step 7 and restart.

The alert’s title reads Update Phone Number, even though there is no opportunity to do so. This may be fixed by Apple later, though I doubt it.

Apple’s email is out of date

The process above was documented using macOS 27, and Apple has made slight tweaks and major improvements over the last few years. However, the company appears unable to shake off the vestiges of the past. Years ago, when you locked your Mac, you had to set a passcode to unlock it. While that isn’t supported with Apple silicon Macs or Intel Macs with the T2 Security Chip, the email Apple sends out still shows a thumbnail screen where you would enter that code and tells you that you can only unlock your Mac with that non-existent passcode.

Tags: Find My, macOS

Apple introduced the 1st-generation AirTag in April 2021 and replaced it with the 2nd-generation AirTag in January 2026. (As usual, there’s no numbering system.) The compact device remains priced the same as when introduced: $29 each, or a batch of four for $99. (By not raising the price since then, Apple has effectively dropped the price by 20% due to inflation.)

While Apple stopped selling the 1st-generation AirTag, you can buy them while supplies last from online retailers, which seem to identify them as 1st generation.

Apple has almost entirely abandoned model numbers for their hardware, with the exception of Apple Watch and AirPods—though even with AirPods, they use a generation number within a particular series number! The same is true with AirTags: the original AirTag is the 1st-generation AirTag (2021), and the new one is the 2nd-generation AirTag (2026). In product and sales information, the new model is simply referred to as AirTag.

If you’d like to tell the difference between the two while looking at them, you can examine the reverse. While there’s no version number, Apple printed distinct information on the plastic silver battery cover. Note that the 2nd-generation AirTag uses nearly all uppercase or capital letters, includes the IP67 designation, and omits the “Designed by/Assembled in” details.

There are four technical differences between the two generations:

  • Louder speaker: Apple says that the new model is 50% louder. The frequency of its chime, the sound you can trigger to locate it (see how to play a sound), is also higher-pitched (moving from an F on the chromatic scale to a G). These two changes allow it to be heard from farther away, from the inside of, or underneath things, like inside a piece of luggage or under a pile of clothing.
  • Greater Precision Finding distance: A 2nd-generation ultrawideband (UWB) chip that appears in the iPhone 17 series, the iPhone Air, the Apple Watch Series 11, and the Apple Watch Ultra 3 allows Precision Finding at “from up to 50 percent farther away than the previous generation,” says Apple (see how to use Precision Finding). In practice, this might mean several dozen feet (or 20 to 30 meters) compared to 30 to 50 feet (10 to 15 meters).
  • More powerful Bluetooth: Some features of an AirTag work only within Bluetooth range, such as playing a sound or live finding before Precision Finding kicks in, if available. The 2nd-generation AirTag has a newer Bluetooth chip that expands its range as well as allowing greater penetration through objects. Apple gives no guidance on distance, but if you could previously reach an AirTag over 150 feet (46 m), conceivably that could now be as much as 300 feet (91 m).

Bluetooth is also used to broadcast an encrypted transmission as part of the Find My network, and could improve tracking as the signal could reach more devices.

  • A lack of backwards compatibility: The new AirTag requires iOS 26.2.1/iPadOS 26.2.1 or later to pair with an iPhone or iPad. Once activated, iOS 26, iPadOS 26, macOS 26, or watchOS 26 or later is required to track the items—maybe even the 26.2.1 release of each of those operating systems, but Apple has conflicting information. This means people using older versions of these operating systems will be unable to track an AirTag. If you have mixed generations of gear or have opted not to install some of the version 26 or 27 releases, you might see 1st-generation AirTags on some devices and 2nd-generation AirTags on others.

For most of the purposes of the rest of this book, you can consider a 1st- and 2nd-generation AirTag as interchangeable. I call out differences only where they exist.

What is inside an AirTag

An AirTag uses three different pieces of wireless technology, somewhat shocking for such a small piece of equipment:

  • Near-field communications (NFC): NFC allows a device to read information from an item held very near or literally tapped against the device. NFC is used to identify an AirTag: the NFC tag can be read by any smartphone with NFC technology, and triggers the display of a webpage link connected to that AirTag.

Every Apple Find My item has a unique serial number. The webpage retrieved via an NFC tap is associated with that serial number. You also can open that webpage from a link transmitted via Bluetooth after being warned that an Apple or Google item is moving with you.

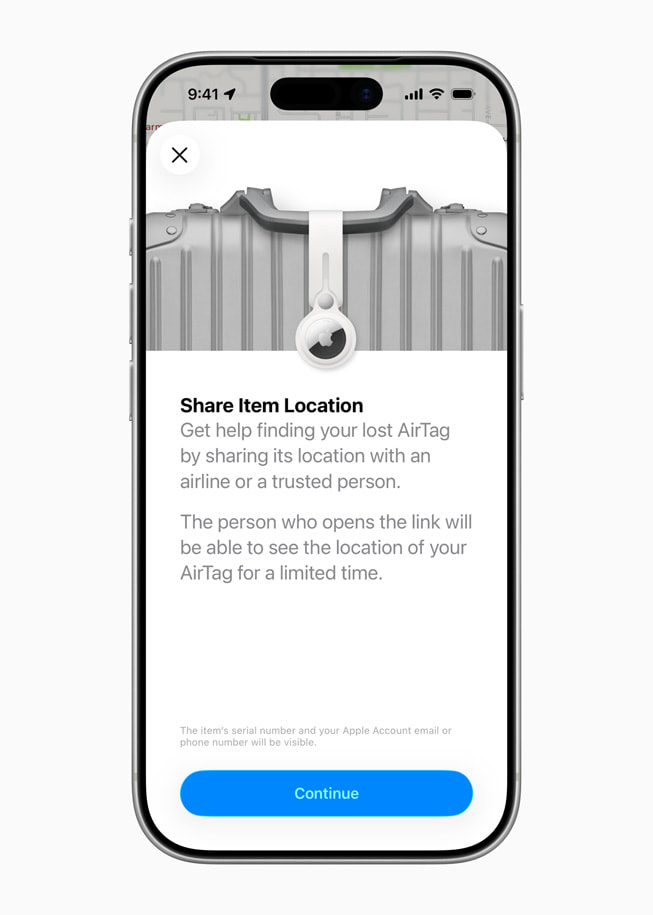
The page shows the serial number and a portion of the person’s phone number registered to their Apple Account or Google Account. For more, see how Apple and Google detect an unwanted AirTag. Starting in iOS 18.2/iPadOS 18.2 and macOS 15.2 Sequoia, you can also opt to create a secure tracking link you can share with anyone that also includes email address or phone number in full. See what someone sees when they find your lost device.

  • Ultra-wideband (UWB): UWB is a low-power, broad-spectrum wireless technology introduced by Apple in the iPhone 11 series and Apple Watch Series 6 and later, and, for audio, starting with the charging case of the AirPods Pro (2nd generation). With the right model of iPhone or Apple Watch, you can pinpoint an AirTag or an enabled charging case with Precision Finding, which provides ranging distance and direction. Which models depend on your generation of AirTag; see how to use Precision Finding.
  • Bluetooth LE: A low-power version of the short-range Bluetooth standard lets AirTags announce themselves to a nearby paired iPhone or iPad and to devices that are part of the Find My network. The 2nd-generation AirTag has a more powerful Bluetooth radio.

Apple does occasionally update the AirTag firmware. However, there’s nothing you can do to force that. With whatever logic the company uses, it sends the firmware update out over Bluetooth when it detects AirTags paired with your devices that are out of date.

Size, battery and price

Apple powers the AirTag with a replaceable battery that should last a year. Both generations of AirTag are identical in dimensions and weight: 1.26 inches (32 mm) in diameter, 0.31 inches (8 mm) thick at their widest point, and 0.39 ounces (11 g).

You can personalize your order when ordering directly from Apple by adding an emoji or a few numbers or letters. You might think the emoji or text is a gimmick. But if you buy several AirTags, it can help you distinguish among them. Bonus: When you pair an AirTag, Apple shows you the emoji or text that’s printed on the item in the pairing screen! Nifty.

Tags: Find My, iOS

To view your device’s location, those of people in a Family Sharing group, or your items, use the Find My app on an iPhone, iPad, Mac, or Apple Watch, or the Find Devices app in watchOS 26 or earlier or on iCloud.com. By activating Find My, you’re signed in to the app on all those operating systems and on iCloud.com. Each view in the iPhone, iPad, and Mac Find My app provides access to a different category of location-finding.

The map in each view includes typical actions, such as zooming in and out, switching to satellite view, and switching to 2D view. The icons, such as the Choose Map and 3D view buttons, appear the same as in Apple Maps.

Those Find My views are separate apps on an Apple Watch running watchOS 26 or earlier: Find People, Find Devices, and Find Items. If I mention a view, find the app in watchOS 26 or use Find My in watchOS 27.

You can add a Find My widget to the Home screen or Notifications Center to see people and devices without opening the app.

The three status labels

For each category—People, Devices, and Items—Find My shows the last time a location was updated in the list: to the right of the item on an iPhone/iPad and under the item on a Mac, Apple Watch, and (for devices) on iCloud.com. It also displays this information in the detail view for the selected item.

Here’s what the status messages mean:

  • Live: Devices can provide a continuous stream of location information in the right circumstances. You can watch someone walk down a street or see their train move across the landscape. (Frankly, a little creepy, even though it’s done with permission?)
  • Now: If live updates aren’t possible due to battery, location, connectivity, or operating system version, Now is the second-best. It indicates an update within the last minute.
  • Time duration: Find My shows X minutes ago or a specific date and time for the last location update.

Selecting an entry

Starting with the version 27 releases, you select an entry by tapping or clicking it. This reveals slightly more information, such as a Directions button or a Play button to play a sound. Tap or click the More button to reveal the sheet of actions for that category.

Before the version 27 releases, Apple had two distinct methods for selecting an item from the people, devices, or items list: one for the Find My apps on iPhone, iPad, and Apple Watch; another for the Mac Find My app.

In iOS 26, iPadOS 26, and watchOS 26 and earlier, tapping an entry selects it and causes its sheet to appear. In macOS 26 and earlier, click the item, then click the Info button to reveal the sheet. macOS 26 and earlier also let you Control-click/right-click an entry to reveal several menu items; macOS 27 limits these to just Remove and, for People, Add to Favorites or Remove from Favorites.

What iCloud.com cannot do

You can’t track people or items on iCloud.com, only devices (via the Find My link, which takes you to the Find Devices app). However, iCloud.com’s Find Devices web app is useful for one purpose: when a device is missing or stolen, and the person whose device it is lacks access to Find My on any of their devices. See how to find a lost iPhone or Mac.

Because of the fraught nature of putting your devices or services on them directly in the path of the entire internet, it’s almost always the case that you can share files more easily, with more control, and more securely using a cloud-based sharing service, with a lot of provisos that I describe along with each service.

Each of these services partitions access, so you know precisely what you are letting someone view or download, and whether they can modify, delete, or upload files. You can set a time limit that a link will work, and usually restrict whether something can be downloaded or just viewed online. You may also be able to tell when they access or view files and see exactly what changes they make, if they have permission to modify files.

All the major tech companies offer them, and you may already have free access to substantial storage, or already be paying for a subscription plan or higher level of storage for other purposes.

All these services encrypt data at rest and use encrypted transport (HTTPS, primarily) for uploads, downloads, and link creation. However, if someone can access your account, they can view, delete, modify, download, and add files without restriction.

If you want to share files in a truly secure, end-to-end manner, however, the gold standard is end-to-end encryption (often abbreviated E2EE). With E2EE, the ecosystem you use generates and retains keys only at endpoints, on devices under your control. (Sometimes you’re involved in generating them, but usually the key creation and management is silently handled by the software.)

iCloud.com was never protected by E2EE before December 2022; after that, it became optional for some services if you enabled Advanced Data Protection (ADP). With ADP, iCloud Drive and other items synced, shared, and available via iCloud.com are protected by E2EE for you and with people with whom you share—so long as they also have ADP enabled. See how to turn on Advanced Data Protection.

Layer your own encryption on top

If you or your shared partners don’t have ADP enabled or can’t turn it on, you can layer E2EE on top of standard secure cloud services, because data that’s encrypted before transfer and stored in these locations remains encrypted, and is only decrypted by endpoints that have the keys.

That is, if you have an encrypted disk image and upload it, that integral encryption isn’t stripped off. If someone downloads the disk image, they still have to break the encryption applied to that data to access what’s inside.

But you can be more sophisticated than a disk image. Software that handles its own encryption—say, the password-management app 1Password—can safely hold and sync its separately encrypted data on a sync service. Someone stealing your 1Password vault has stolen trash.

As of 1Password 8, the app works only with its own syncing system. It used to work with Dropbox and iCloud.

Beyond software that uses E2EE for its internal format are packages that allow generic file sync by effectively tunneling the end-to-end encryption across a sync service! From your perspective, the files are readily available; to everyone in between you and your devices, including the sync services, it’s just a bunch of garbage-looking data. This is a nifty workaround.

I can’t recommend a service, as I don’t use any, but there are two options you can test for this purpose that are Mac compatible:

  • Cryptomator is an open-source solution to create an encrypted package, called a vault. It’s free to use on Mac, Windows, and Linux. The Android and iPhone/iPad apps have a one-time €19.99 (about US$23) purchase price to cover development costs.
  • VeraCrypt is also free, open-source software for creating virtual encrypted disks or partitions. However, the project supports desktop operating systems only: Linux, macOS, and Windows.

Cloud sync services usually reduce data transfer required by syncing only changed portions of files. (Unix folks call it the diff after a command-line tool; delta encoding is a more exact technical term.)

With encrypted files you upload, large portions of the file or the entire file change whenever it’s modified, resulting in a lot of data synced. However, Apple’s bundle form of disk images and some third-party software breaks large files into smaller ones to solve this problem. Only those sub-portions are changed, resulting in less syncing.

Encrypted messaging with others

Apple enabled E2EE with Android users for messaging over RCS, an industry standard Google championed. However, be sure to check when you start messaging with someone using RCS that their Android device has RCS encryption enabled. You can see whether it’s enabled in Messages: an Encrypted label appears at the top of the conversation, or inline if the encryption method changes. (If you had an ongoing conversation with someone over RCS, upgraded your device, and they have encryption enabled, an inline message in the conversation would appear.)

If you want to use E2EE to exchange data with others, you can use options like GPG Suite ($23.90 per year, 30-day trial, Mac only), which manages public-key encryption data for you, and lets you exchange encrypted files via email with anyone else who uses PGP- or GPG-compatible software. (PGP is a decades-old implementation of public-key encryption; GPG is the GNU, free-software version.)

If you trust other parties to manage the process, you can use iMessage or Signal. In early 2021, Apple quietly overhauled iMessage’s innards to make it more robust, but still needs to publish its spec and allow outside auditing. The company quickly had to patch major exploits found in their update in September 2021, making an even better case for allowing more eyes on the problem.

In May 2025, people were baffled that they couldn’t type “Dave & Buster’s” and similar ampersand-containing names into Messages. Turns out, Messages transformed the ampersand into something that triggered the protection! Apple fixed it, but it showed it worked?

Despite Apple’s lack of full transparency, iMessage remains trustworthy. Signal is created by an organization devoted to privacy, and has proven itself a great way to avoid interception.

What if you’ve lost your Apple hardware and it’s in a place where it can’t reach a Wi-Fi network and either has no active cellular data plan or can’t reach a cellular base station? What if it’s stolen, and the thief has disabled network access through Control Center? What if you stuck an AirTag or other Find My item on your backpack and left it where you can’t remember—or it was taken from you at an unknown time?

Apple’s solution is anonymity-preserving crowdsourcing that relies on the billion active devices their customers use worldwide, running recent-enough versions of iOS, iPadOS, and macOS to participate. The system relies on devices that can’t connect with the internet or a paired device to begin transmitting an anonymized, encrypted Bluetooth network signal that other Apple hardware can pick up.

A user's iPhone 17 Pro shows a screen that reads

Find My crowdsourcing causes every supporting device or item to emit a Bluetooth beacon that incorporates an encrypted hardware identifier.

This ID changes at regular intervals to prevent the privacy or safety nightmare of a third party tracking you, your devices, or your items through a persistent ID. Even Apple doesn’t really know where your devices and items are when using crowdsourcing!

When a device or item sends this beacon varies between Apple devices and Find My items:

  • iPhone, iPad, Mac, or Apple Watch: Find My must be enabled on the device (including the Find My network option), and it must be unable to make a connection to the internet.
  • AirTags and other Find My items as well as Apple and Beats audio hardware: If the audio hardware is within Bluetooth range of its paired device, it acts like a device, relaying its location through it. When beyond that range, it broadcasts a Bluetooth beacon as if it were a Find My item.

While 2nd-generation AirTags have minimum operating system requirements to appear in Find My apps, there is no such issue for the Bluetooth signals they broadcast. Any device that can relay a 1st-generation AirTag’s location can relay that of a 2nd-generation AirTag. (See AirTag 2 vs AirTag.)

The original AirPods rely solely on Bluetooth-based location tracking. When within Bluetooth range, they appear in the Find My app under Devices. However, they don’t work with the crowdsourced network. You can’t mark those audio devices as lost, and you can find those devices only within range of their paired iPhone or iPad.

What Apple can and cannot see

This broadcast is recognized by anyone’s iPhone, iPad, or Mac running at least iOS 13/iPadOS 13 or macOS 10.15. If a device owned by another person has an internet connection, it encrypts a package containing the beacon’s name and location information obtained or inferred, and uploads it to Apple.

That information is stored in a very particular way:

  • Apple doesn’t track what IP address or device uploaded it.
  • Apple doesn’t know to which device or Find My item any Bluetooth ID is associated—only your hardware retains that.
  • Apple doesn’t have encryption keys to extract location information.

It’s a beautiful system, in that no one—not Apple, the other equipment’s owner, or anyone sniffing in the area near your device—can determine who the hardware belongs to.

In the right circumstances using an iPhone, iPad, or Mac native version of the Find My app (see Precision Finding), you trigger retrieval of this location and timestamped location:

  • The Find My app uploads a cryptographic secret that Apple can match against the encrypted bundles they have of Bluetooth ID and location.
  • Apple’s servers transmit matching entries to the requesting device.
  • Using a locally stored encryption key that only your devices possess, the bundles are unlocked to determine the last location found.

What you get back

Find My provides this information in two different ways depending on the hardware you’re using:

  • iPhone, iPad, Mac, or Apple Watch plus audio hardware: The current location appears as expected in the Devices view of a native Find My app. If the device has an internet connection (direct or via a paired device for audio hardware), its location is a directly provided one; if it’s not connected to the internet, the Find My location appears when you use a Find My app.
  • AirTags and other items: The current or last-tracked location of a Find My network item, whether from a paired device or anyone else’s Apple device, is always shown in the Items view of the Find My or Find Items app. If you mark these devices as lost, you have more options: see what someone sees when they find your lost device.

In contrast to the Find My Device service, the Find My network is almost entirely one-way: you can determine where something is, but an owner can’t send a signal to the device unless it’s within Bluetooth range of an owner’s device. It also can’t be locked or erased as with internet-based Find My actions; See how to play a sound on a lost device or AirTag.

There are two actions you can perform as the owner of a Find My item:

  • When marking an item as lost, you can provide a phone number that Apple also stores securely. Someone finding the item can retrieve that data from Apple.
  • When you are near enough to connect to an item from one of your devices via Bluetooth, you can play a sound on it. This is particularly useful for finding a lost item in a classroom, home, or car, or for being notified of one nearby.

If someone’s iPhone or iPad detects that a Find My item or a Google Find Hub item is moving along with them—determined by Bluetooth proximity and across time—they are offered the opportunity to play a sound. That signal is sent via Bluetooth. (The same is true for an Android device detecting an Apple Find My item.) See what an “AirTag Found Moving With You” alert means.

Apple Designed the Find My Network To Deter Stalking

You might conclude that the design of the AirTag and other Find My items is both great for finding your own lost or stolen stuff—and a way someone might deploy tracking against you.

Fortunately, Apple included design elements in their Find My network for AirTags and third-party gear to try to protect the privacy of those who might be under observation without their knowledge, or who wind up accidentally transporting them. I dig into this in depth in Understand Stalking via Tracking.

Industry-Wide Anti-Stalking Standard Launched

Apple developed their system independently, though it offers a license and access to third parties. Facing criticism from a range of politicians and groups about stalking by tracker, Apple and Google—joined by several smaller firms—released a plan for interoperable industry support for identifying trackers across networks that went into effect in operating system and item updates in 2024. For more, see Active Stalking and an Industry Alliance.

You can also enable separation alerts. This feature notices when any Find My device or item is no longer in proximity to your iPhone or iPad. This might happen if you leave an iPhone in a coffee shop or it slips out of your pocket in a movie theater or you forget you put your iPad in an airplane seat’s unhygienic publication pocket. I explain separation alert management in Notifications for Devices and Items.

Google’s Find Hub offers a competing, non-interoperating ecosystem. Apple and Google don’t share location data with each other’s networks. But Android phones, iPhones, and iPads detect unwanted trackers across both ecosystems. See how to check whether someone is tracking you.

Apple introduced a hidden flaw when they made it possible to use your iPhone or iPad to reset the password for your Apple Account. There was a perfectly good reason to make this linkage: if you could access the password-changing part of the interface, that meant you possessed your device, could unlock it via your face, fingerprint, or passcode, and had the passcode for further changes.

If Apple hadn’t let people reset their Apple Account password with their device, they would have potentially hundreds of thousands of support calls a year dealing with this issue. Instead, resetting is a relatively trivial matter—easy to find instructions online and easy to help someone with if it requires an Apple Support call or text.

However, through subterfuge or violence, it’s possible to obtain both an iPhone and its passcode, at which point someone could hijack your Apple Account and leverage access to your phone and that account to take over your life.

Stolen Device Protection takes the fangs out of this viper. It has a number of tradeoffs, but it may be worthwhile for additional peace of mind for some people. Here’s what to consider:

  • It is not enabled by default. You have to choose whether or not it’s useful to your circumstances, and then opt in.
  • It’s available only on iPhone, with Apple ostensibly reasoning it’s the most at-risk device for theft coupled with passcode acquisition.
  • While enabled, your iPhone passcode cannot be used for a host of actions related to passwords, payments, tracking, and erasure. You must use Face ID or Touch ID.
  • Apple imposes a new one-hour delay between when you want to make certain kinds of Apple Account, biometric, passcode, or tracking changes and when you are allowed to make them.

Starting in iOS 18, if you turn off or restart your iPhone, the timer restarts, counting down again from a full hour. That new hour is counted from when your device finishes its restart cycle or from the next time you power it up.

That sounds a bit annoying, no? Well, here’s the kicker: when enabled, the biometric requirement for some features and one-hour delay for others apply by default only when you are in an “unfamiliar” location. That’s right: Apple uses secure device-based stored information—to which they don’t have access—to determine whether you’re at a place you regularly linger at, like home, work, or a neighborhood pub. If you aren’t, the extra protections are enabled automatically.

Many news outlets reported that Apple enabled Stolen Device Protection by default in iOS 26.4 in early 2026. However, I never saw any confirmation from Apple, or follow-up from the news outlets. Further, I installed iOS 27 on an erased phone and Stolen Device Protection was off when the iPhone first started up.

That means when you’re at a familiar location, you won’t notice at all that Stolen Device Protection is on. If you return while using your device from an unknown to known location, the restrictions drop, too. You can opt to disable this “familiar location” feature, too, if you want the same level of deterrence everywhere.

Should you enable it?

Even though not everyone needs the feature enabled, I’d argue that if you go out into the world, it’s possible you’d be shoulder surfed and robbed, so if you have any interest in staying safe, you should probably turn it on and deal with the inconvenience.

To enable Stolen Device Protection on your iPhone, you first have to ensure all the following conditions are met:

  • Two-factor authentication for your Apple Account: Nearly all Apple Accounts have this enabled already. If yours isn’t, Apple’s support site explains how to switch it on.
  • A device passcode enabled plus Face ID or Touch ID: It’s highly unlikely you have no passcode. See how to set up Touch ID and Face ID.
  • Find My enabled: I recommend this for everyone, and it’s specifically required for this feature. Go to Settings > Account Name > Find My.
  • Significant Locations & Routes enabled: Enable via Settings > Privacy & Security > Location Services > System Services > Significant Locations & Routes. (Significant Locations & Routes are derived from your iPhone, stored locally and securely, and never sent to Apple or anyone else.)

To enable Stolen Device Protection, go to Settings > Face ID & Passcode > Stolen Device Protection. Enable the feature. You can optionally switch from Away from Familiar Locations to Always to ignore Significant Locations & Routes and always have restrictions.

Once it’s enabled, there’s a laundry list of things you cannot do when away from a familiar location (or always, if chosen).

You must use Face ID or Touch ID for the following: to retrieve passwords or passkeys, use Safari’s AutoFill stored payment methods (like credit cards), disable Find My’s Lost Mode (see below), erase the device (Settings > General > Transfer or Reset iPhone > Erase All Content and Settings), remove hardware security keys, add trusted phone numbers for two-factor authentication codes (see how to prepare for losing access to your Apple Account), apply for an Apple Card or view its virtual card number, transfer money via the Wallet (like transferring money out of your Apple Savings account), or use Quick Start or other migration tools to set up a new device.

The one-hour security delay

Across the entire history of Touch ID and then Face ID, Stolen Device Protection is the first time Apple has deferred to a biometric authentication method and disabled your passcode. In all similar cases, biometrics are either unavailable and you must use a passcode, or your iPhone, iPad, or Mac allows you to decline biometrics and enter a passcode.

The security delay of an hour works like this when you’re somewhere your iPhone thinks is unfamiliar, or you’ve disabled it:

  1. Attempt to make any of the following changes: with Apple Account, change your password, sign out on the device, or update security settings; or try to remove or change Face ID or Touch ID, change your iPhone’s passcode, reset settings (Settings > General > Transfer or Reset iPhone > Reset), disable Find My or, of course, disable Stolen Device Protection.
  2. Your device prompts you to authenticate with Face ID or Touch ID.
  3. You’re prompted to wait for an hour. Tap Start Security Delay, and a counter starts. You can also return to a familiar location within that period.
  4. When the hour is up, you receive a notification. Tap it or return to the feature in question and use Face ID or Touch ID to complete the authentication.

If Touch ID or Face ID works erratically for you, as it does for some people, you could wind up being unable to perform a number of tasks until you’re back at a familiar location.

You can disable Stolen Device Protection at any time by returning to its settings for your version of iOS. As noted above, if you’re not at a frequently visited location, it will require an hour delay to disable it. (But why would you disable it when at an unfamiliar spot?)

If you’re away from a frequently visited location and your Touch ID or Face ID stops working, you can be completely stuck until you have a way to access an iCloud backup from another device or return to a familiar spot. Apple doesn’t describe any way to override the biometric lockout except by being somewhere “familiar.”

Tags: iOS, Security

Activation Lock is an Apple feature designed to deter theft by preventing erasing and re-using an iPhone, iPad, Mac, or Apple Watch that has Find My enabled. While someone can still erase a device with Find My turned on, they are unable to activate and use the iPhone or iPad without having the Apple Account password for the account with which the device was used. Thieves have some hardware tricks to bypass this, unfortunately, but they don’t always work.

A device with Activation Lock active can still be tracked via Find My even after it’s been erased! And Apple will display a screen to any potential buyer or other user that the device is locked, deterring thefts and duped buyers.

Activation Lock was first released in 2015, and works with the iPhone 5s and later and iPad Air and later. An Apple Watch needs to run watchOS 2 or later. Macs models that support Activation Lock must either have a T2 Security Chip (Intel) or use an Apple silicon processor; in either case, macOS 10.15 Catalina or later must also be installed.

Even AirTags have a sort of Activation Lock—the Find My Lock—which is covered in how to reset an AirTag.

To avoid this when selling an iPhone (or associated Apple Watch), iPad, or Mac, disable Find My before erasing, which requires entering the associated iCloud account’s password. (Apple prompts you to disable Find My before letting you erase your device.) You can also disable it via iCloud.com after a device is out of your hands. Once you disable Find My, tracking is off.

If you haven’t disabled Find My on a device and you lose access to your Apple Account, the device remains permanently locked as well.

When purchasing any used Apple hardware, ensure that Activation Lock was disabled before you pay!

Remove a device from your account

You might see devices in this list that you or your family member no longer possess or that no longer work. You can remove these items from your Apple Account in any of several places. This removal also disables Find My on the device if it’s connected to the internet or the next time it connects.

Starting with the version 27 releases, use your iPhone, iPad, or Mac if you want to remove a device. (Previously, Find My was the better place to start.) Go to System Setting/Settings > Account Name, then scroll to the bottom. You then tap or click Remove from Account. You’re prompted with an improved warning in the version 27 releases:

  • In any version 27 operating system, Apple asks “Still Have This Device?” and defaults to a big blue OK button. To further discourage you, the dialog explains you should go to the device and sign out directly. Otherwise, tap or click Start Removal.
  • In the version 26 releases and earlier, you’re given a briefing on what happens if you remove the device. Tap or click Remove to proceed.

Apple once warned you that “This Mac will reappear if it connects to the Internet and Find My is turned on.” That warning was clearly inadequate about the consequences!

Some devices may offer a removal button in the Find My app on an iPhone, iPad, or Mac. The Find My app appears to be the only way to remove your AirPods from an Apple Account. However, in both the version 26 and 27 releases, I found it inconsistent and confusing why I was sometimes given a Remove from Account or Remove button, and at other times it was dimmed or resulted in an error message.

For instance, I can’t remove my iPhone, even though I’m offered a button to do so. (This may be connected with Stolen Device Protection, but it’s not described that way.) The Find Devices web app on iCloud.com only shows Erase, not Remove, for all devices except my iPhone, and it produced the same error.

Nonetheless, if you’re in a Family Sharing group, you can remove people’s devices from their accounts via an iPhone, iPad, or Mac Find My app or Find Devices at iCloud.com. (Or remove your device from your account.) The Apple Account password for the device is required, and a second factor may also be requested.

The Apple Account website used to let you remove devices, but now it shows the same error in every case.

AppleCare+ needs Find My switched on first

Apple offers an extended warranty against loss and theft for iPhone, iPad, and Apple Watch owners in several countries: “AppleCare+ with Theft and Loss”; in some countries, it’s the only option for these devices. An iPhone plan is $9.99 per month. In the United States, you can also enroll multiple devices with AppleCare One, and any iPhone, iPad, or Apple Watch on that plan receives theft and loss coverage. These plans start at $19.99 per month for up to three devices with no yearly discount.

This theft and loss warranty covers hardware faults at no cost and breakage for a modest fee. In the United States, it’s $29 to fix an iPhone’s screen or back glass, and $99 for other damage.

For loss or theft of these covered models, you pay a bit more, like $149 for an iPhone or $129 for an iPad. They will even ship you a replacement phone if you’re outside your own country and in a covered country! (You can get replacements only twice in any 12-month period.)

However, there are two key requirements. First, Find My Device must be enabled before a loss or theft occurs. Second, your device must remain associated with your Apple Account until a customer service representative tells you to remove it.

When you call AppleCare customer service to report the loss or theft, a representative guides you through erasing your device via Find My (see how to erase a lost iPhone or Mac remotely), disabling it remotely (Apple doesn’t explain what this means), and then “transferring ownership” to ensure no one can reclaim a “lost” phone later. Read the fine print if you sign up for this warranty option.

Apple expects an AirTag’s battery to work for more than a year. In my experience, it’s somewhere between 6 and 12 months.

Apple once published that 6 to 12 month range. Now, I can’t find it mentioned on their site at all.

To replace the battery, open the case, swap the cell, and close it again:

  1. Remove the back cover: Holding the glossy white front, push down to twist the metal back panel counter-clockwise. It only needs to move a small distance before the cover pops off.
  2. Remove the battery: Inside, you’ll see its small coin cell battery. Remove the battery, making note of the right side up: the + sign on the battery will always face you.
  3. Insert the new battery: Put the new cell in with the + sign up, facing you.
  4. Reattach back cover: Now you can look at the cover to see the extended tabs and align those with the hole in the top. Press in and then rotate the cover clockwise against its top until it’s firmly in place.

The small size of the AirTag, its cover, and the battery within are all choking hazards for small children or pets. If you have either or have visitors with them, keep track of loose AirTags or parts.

Many CR2032 lithium batteries are now sold with a “bitterant-coating”—a coating that makes it bitter to the taste—designed to deter a child who gets one in their mouth from swallowing it. They should spit it out instead. (The same danger is present for pets, though the coating may not fully deter animals from swallowing.)

Apple recommends using a battery with such a coating, and particularly notes that the “Duracell 2032 Lithium Coin Battery with Bitter Coating” works with an AirTag. Manufacturers all use different coating methods, so it’s possible you will buy a battery that will not correctly power an AirTag. I’d recommend buying one or a small package first before making a bulk buy.

The U.S. Consumer Product Safety Commission issued a “Notice of Violation” to Apple in January 2025, because their AirTag and packaging failed to include necessary child-protection warnings required by the March 19, 2024, Reese’s Law, named for a child who died after swallowing a coin-cell. Apple updated their packaging since. The company also provides safety information when the Find My app recognizes a battery reaching the end of its life.

If you are resetting an AirTag rather than changing its battery, the sequence is different. The folks at Elevation Lab have created many kinds of AirTag cases, but perhaps their two most striking are the extended battery models, which come in 5- and 10-year versions. The duration depends on two long-life lithium batteries: AAA for 5 years and AA for 10 years. The rugged case is secured with a screw with a difficult-to-find drive head. The company designed it to be installed in hard-to-reach places to provide maximum protection for an estimated 5 or 10 years.

For those at high risk of being directly and individually targeted by spyware—for example, if you’re a journalist, politician, human rights advocate, or political activist—Lockdown Mode should be on your radar.

Governments, criminals, and industrial espionage agents typically deploy spyware against uniquely identified, high-value targets. Spyware, which largely relies on zero-day exploits, can be deployed as easily as texting someone a message, even if the message is never read.

With spyware installed, a remote operator may be able to exfiltrate (remotely copy off your device) all your data, access your microphone or camera without tipping you off, intercept messages sent by secure apps directly on your device, prevent messages from being sent or reaching you, plant evidence, and much more.

Apple considers spyware a significant violation of personal privacy. While in some countries there are legal methods to deploy spyware, it’s often used in contravention of national laws within countries and for national-security purposes or to violate the human rights of citizens or residents. Often, spyware is used by one country against those living in another country, including travelers, emigres, exiles, or refugees from the first country. China is notorious for pursuing current and former Chinese citizens living abroad. Apple funds researchers who try to uncover the use of this kind of software and protect against it, as part of their internal security work.

As a further effort to block intrusion, Apple added Lockdown Mode, a sort of super-firewall to resist known pathways for exploits by those who find themselves targets. Lockdown Mode works on an iPhone, iPad, Mac, or Apple Watch.

With Lockdown Mode engaged, your device will filter rich incoming media, block metadata, and prevent you from receiving invitations to any of Apple’s services. Messages blocks attachments and will receive and display only text and images, while disabling links and link previews. In Safari, Apple disables certain browser-based features that allow sophisticated code to run in web apps. (You can add exceptions and manage them, too.)

Starting with Apple’s version 26 operating systems, Messages always automatically disables links to URLs and phone numbers in messages the app identifies as spam.

Lockdown Mode also blocks incoming communications and invitations from people with whom you haven’t previously initiated contact. That is, if someone called you via FaceTime and you spoke with them, they will be unable to call you with Lockdown Mode on. If you called them in the past, however, they’ll be able to. SharePlay and Live Photos are also disabled.

Apple also blocks the installation of configuration profiles, often used to shunt network traffic for interception and to bypass security rules, and a device can’t be enrolled in mobile device management (MDM), commonly used in organizations to manage devices; MDM allows remote configuration and the overriding of user settings.

You can’t join a Wi-Fi network when Lockdown Mode is enabled unless the network has a password set. Also, the location is removed by default from images or videos shared in Photos, and Shared Albums aren’t available.

On the hardware side, you have to unlock your device before attaching to a computer or any accessory via the USB or Thunderbolt port. On a Mac, all accessories must be approved, independent of your option for accessory attachment described in the Mac settings worth changing.

How to turn it on

If you are one of those targets or just want to try out this technology, it’s simple to use. Here’s how to turn it on:

  1. Go to System Settings > Privacy & Security > Lockdown Mode and click Turn On next to the Lockdown Mode label, or go to Settings > Privacy & Security and tap Turn On Lockdown Mode.
  2. At the warning screen, read through the extensive list of limitations, and then click or tap Turn On Lockdown Mode. (Click Cancel to exit, or tap the close button.).
  3. Apple provides one additional warning that Lockdown Mode should be enabled on all your devices, and prompts you to click Turn On & Restart—or click Cancel to exit.
  4. Enter your administrator password and click OK. (You may be prompted earlier in the process for this password.)
  5. Your device restarts. On all other devices linked to the same iCloud account you receive a notification or popup dialog that prompts you to restart with Lockdown Mode. You can exit the dialog or click Later. You may receive this warning multiple times at intervals.

Living with Lockdown Mode

After your device restarts and you log in or enter the passcode, you will likely notice few differences.

When you’re browsing in Safari, a Lockdown Enabled banner appears at the top of every page: on the toolbar for a Mac and below the Location bar on iPhone/iPad. If you want to add a given site to the list of ones excluded from Lockdown strictures, Control-click/right-click in the address bar on a Mac and choose Settings for site name. Uncheck Enable Lockdown Mode. On iPhone/iPad, tap the Page Menu button in the address bar and tap the More button, then disable Lockdown Mode. You’re prompted to confirm your choice with an explanation of what that means. The banner on that page now reads Lockdown Off in red type.

You can change which websites are excluded from Lockdown Mode in Safari > Settings > Websites > Lockdown Mode on a Mac. This view shows both open websites and those you made a choice about. In this context, On means that the site has Lockdown Mode protections enabled, while Off means you have disabled any such protections for that site.

On an iPhone or iPad, go to Settings > Apps > Safari > Lockdown Mode, where you only see websites listed that you specifically disabled Lockdown Mode protections. Website exclusions don’t sync across platforms, either.

Outside of Safari, you’ll notice the difference when you attempt to perform an action that’s not permitted in Lockdown Mode. For instance, try to install a profile or view a file attachment in Messages, and you see descriptive error messages.

After you restart with Lockdown Mode disabled, you still won’t be able to open anything blocked in Messages on that device. Double-click a file and you see the same error.

To disable Lockdown Mode, follow the steps above and click Turn Off or tap Turn Off Lockdown Mode and then confirm by clicking or tapping Turn Off & Restart. You should be asked to authenticate via Touch ID or using a password. Your Mac restarts as normal and has full functionality re-enabled.

Apple’s withdrawn lawsuit

Apple sued an Israeli company offering spyware software to governments, but abruptly withdrew the suit in September 2024. They said in their filing, “Any disclosure, even under the most stringent controls, puts this information at risk. Due to the developments since this suit was filed, proceeding forward at this time would now present too significant a risk to Apple’s threat-intelligence program.”